

Indoor
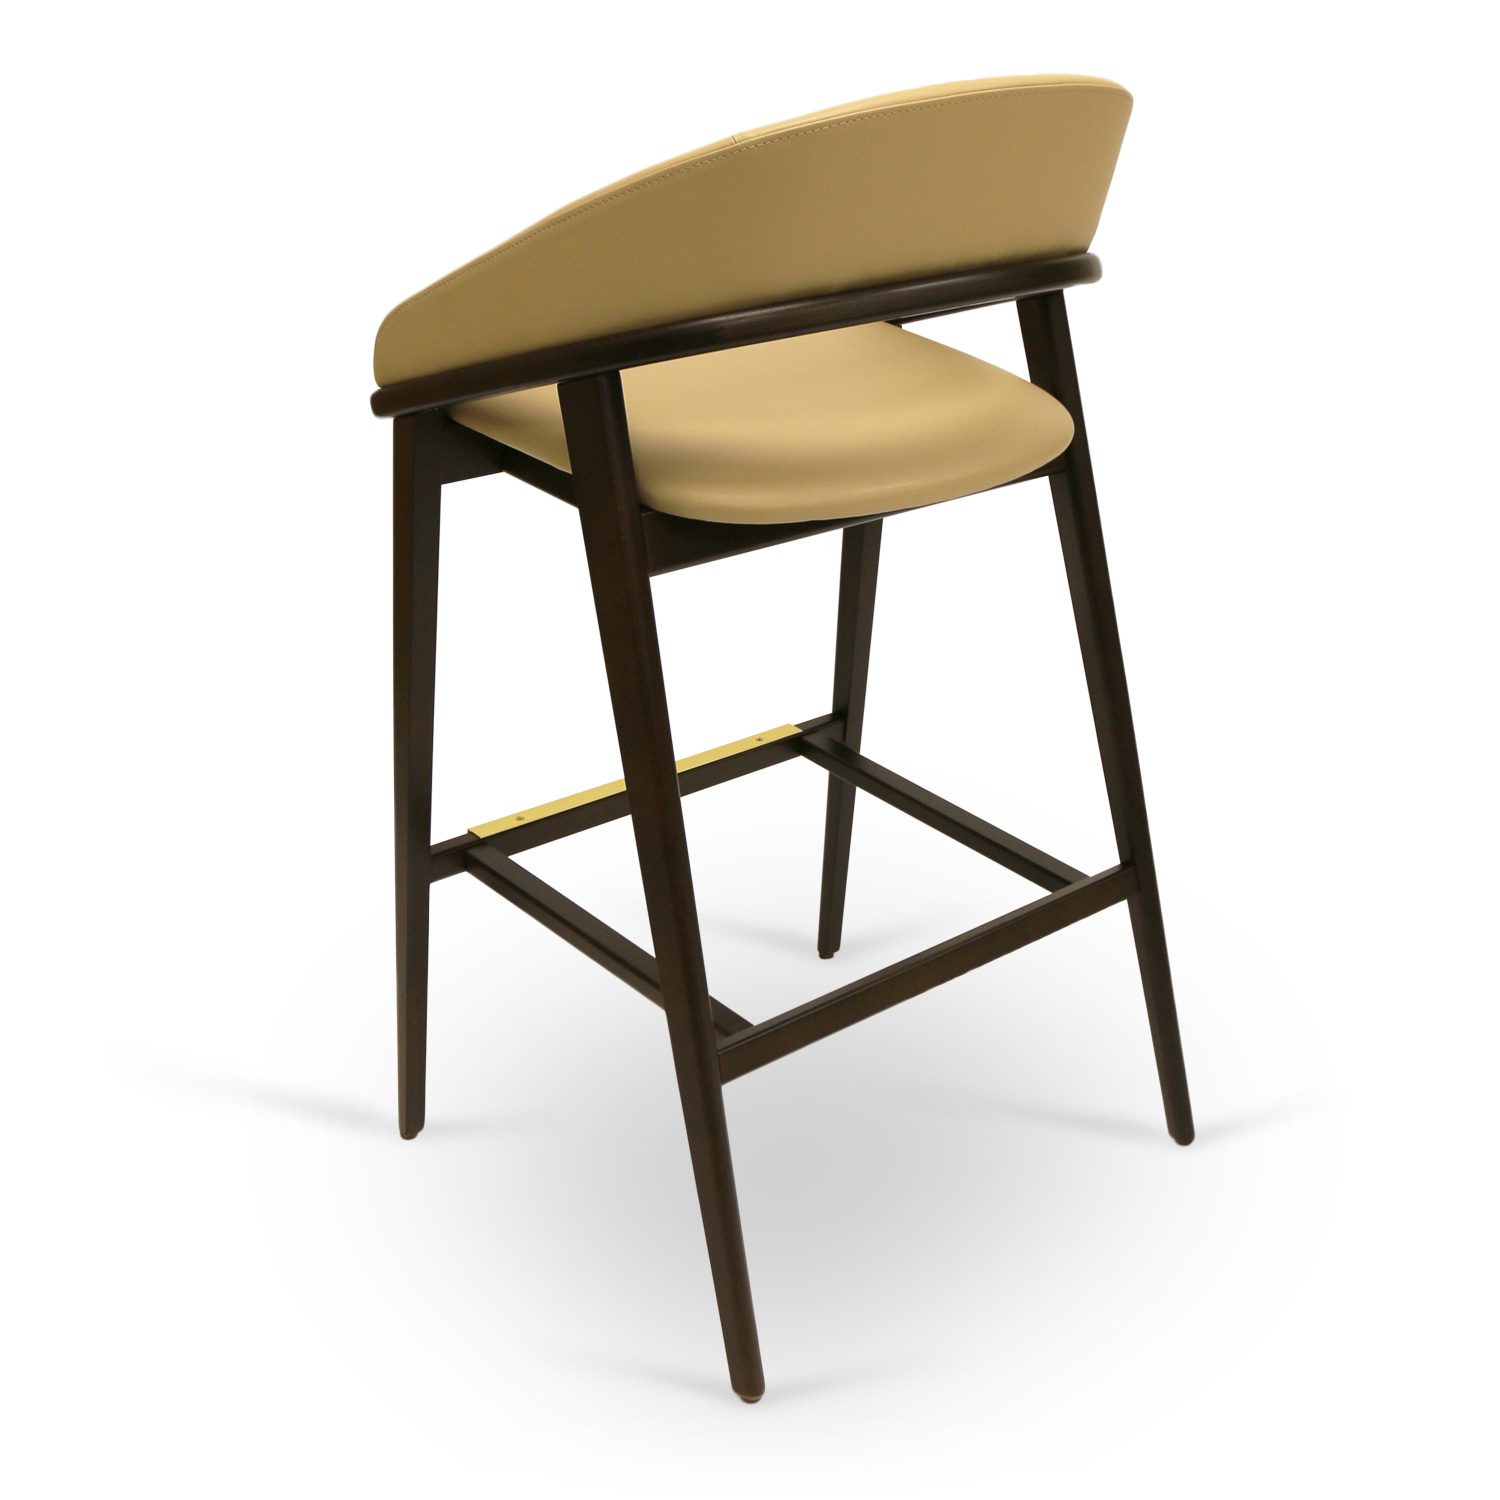
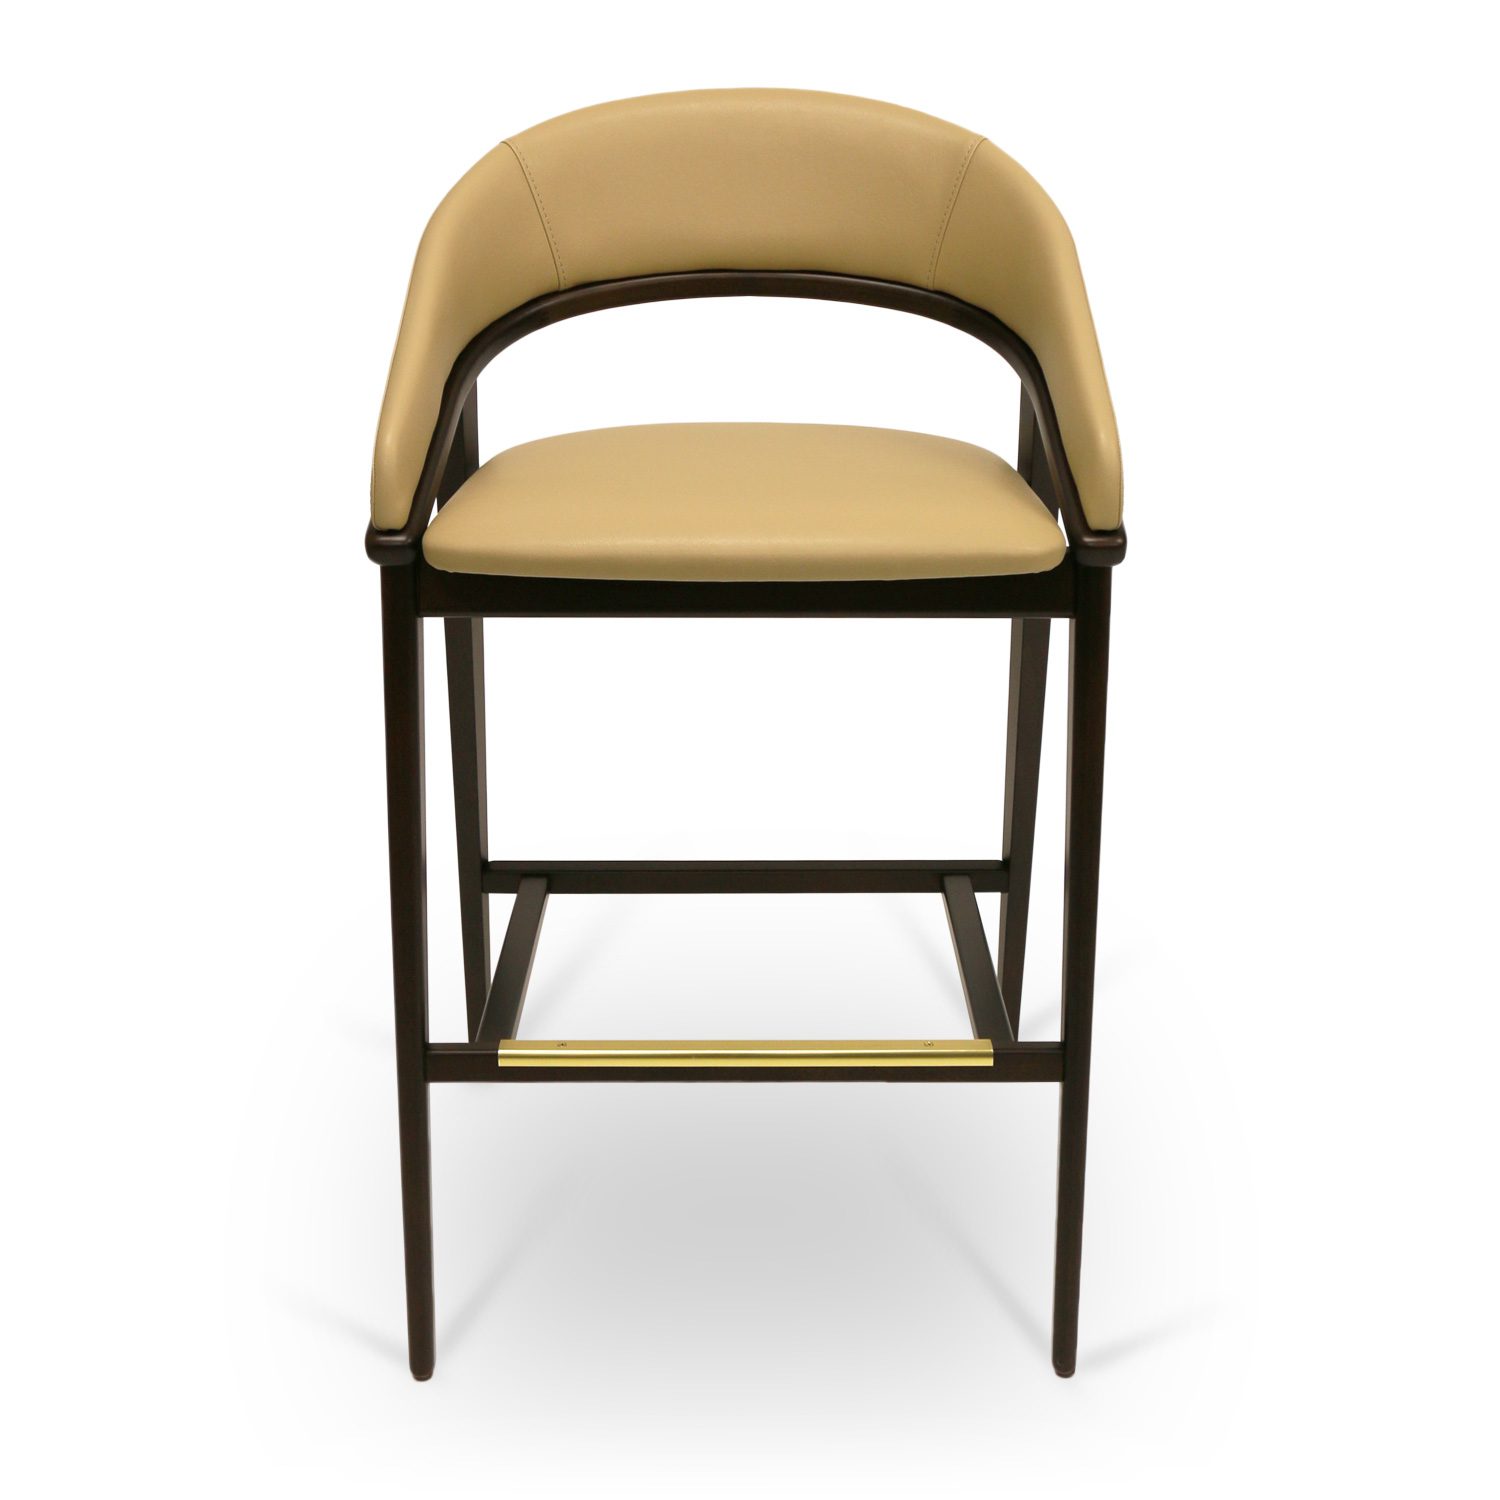
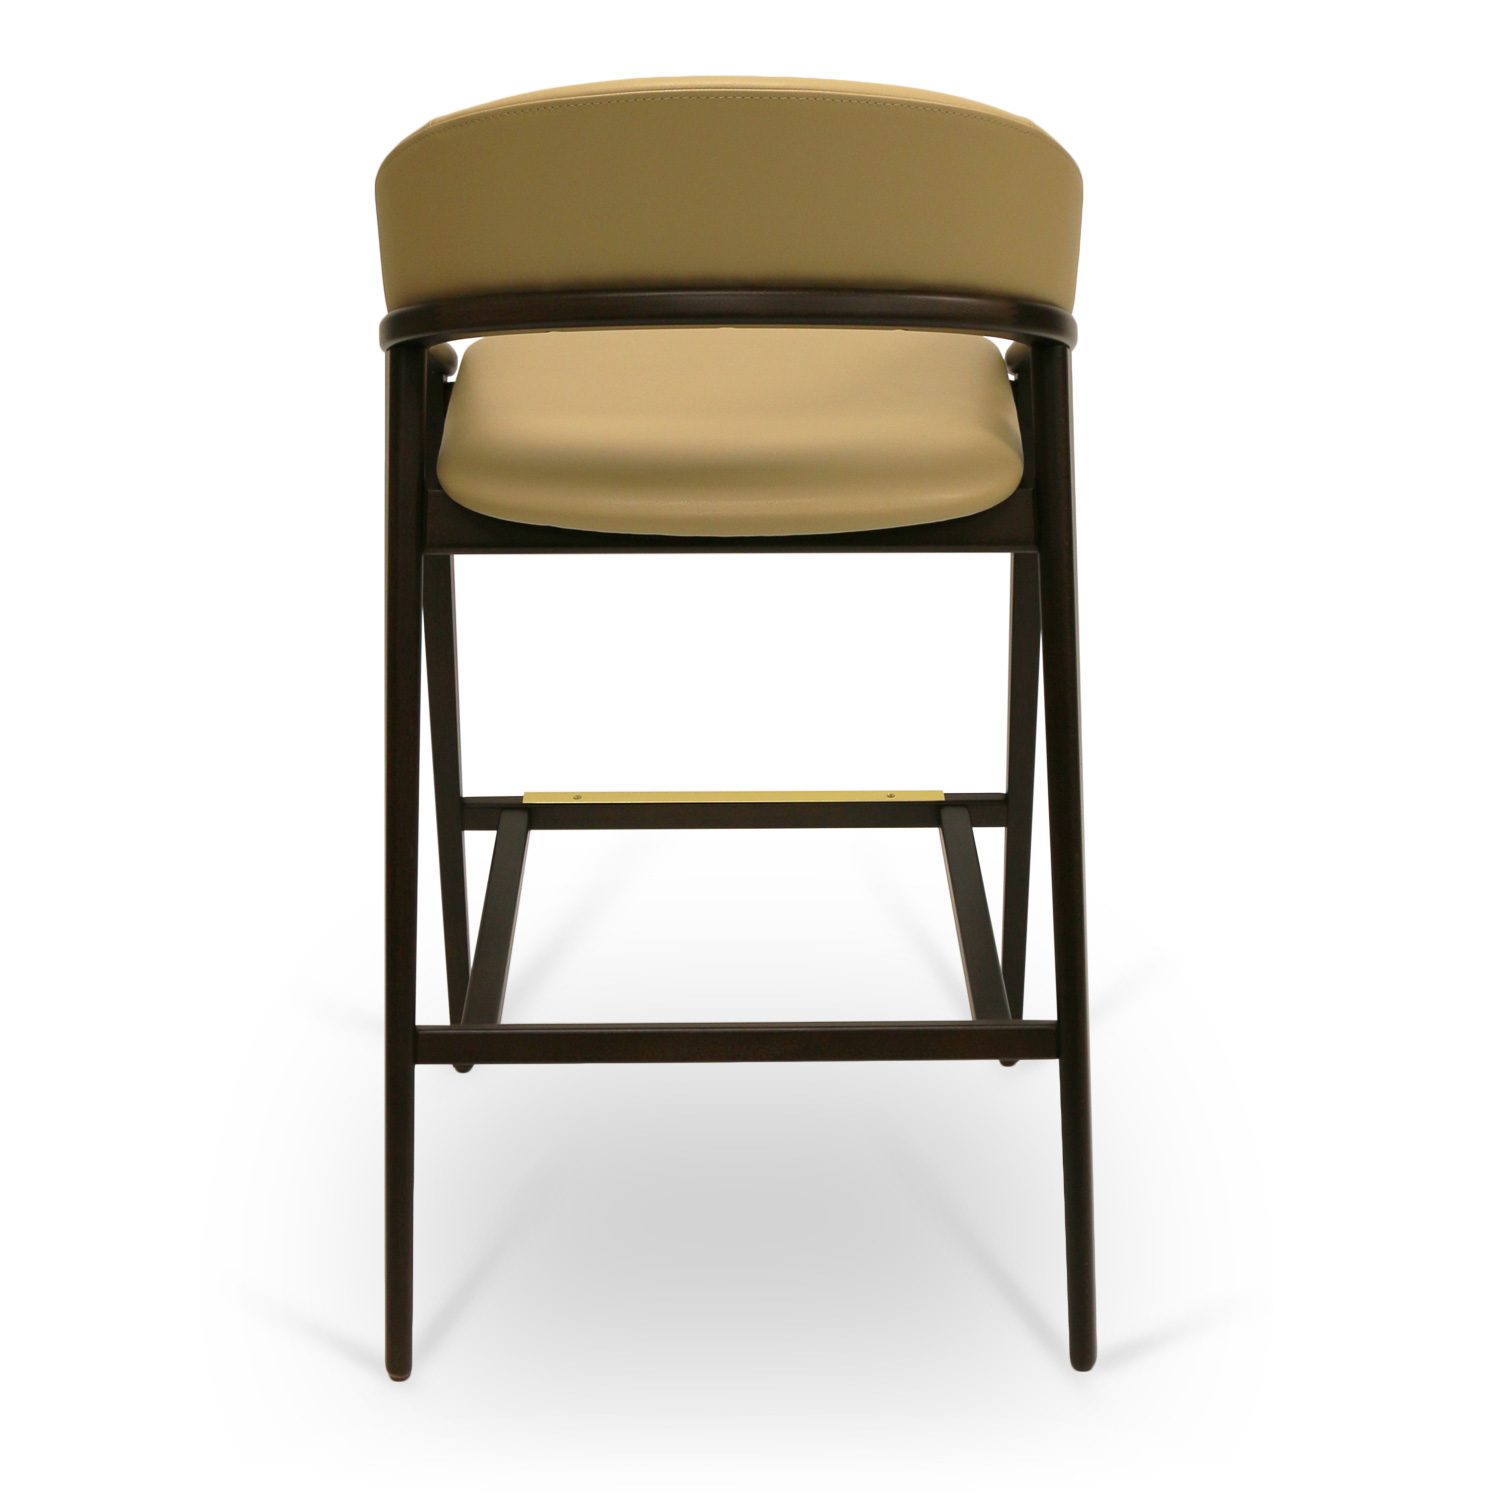
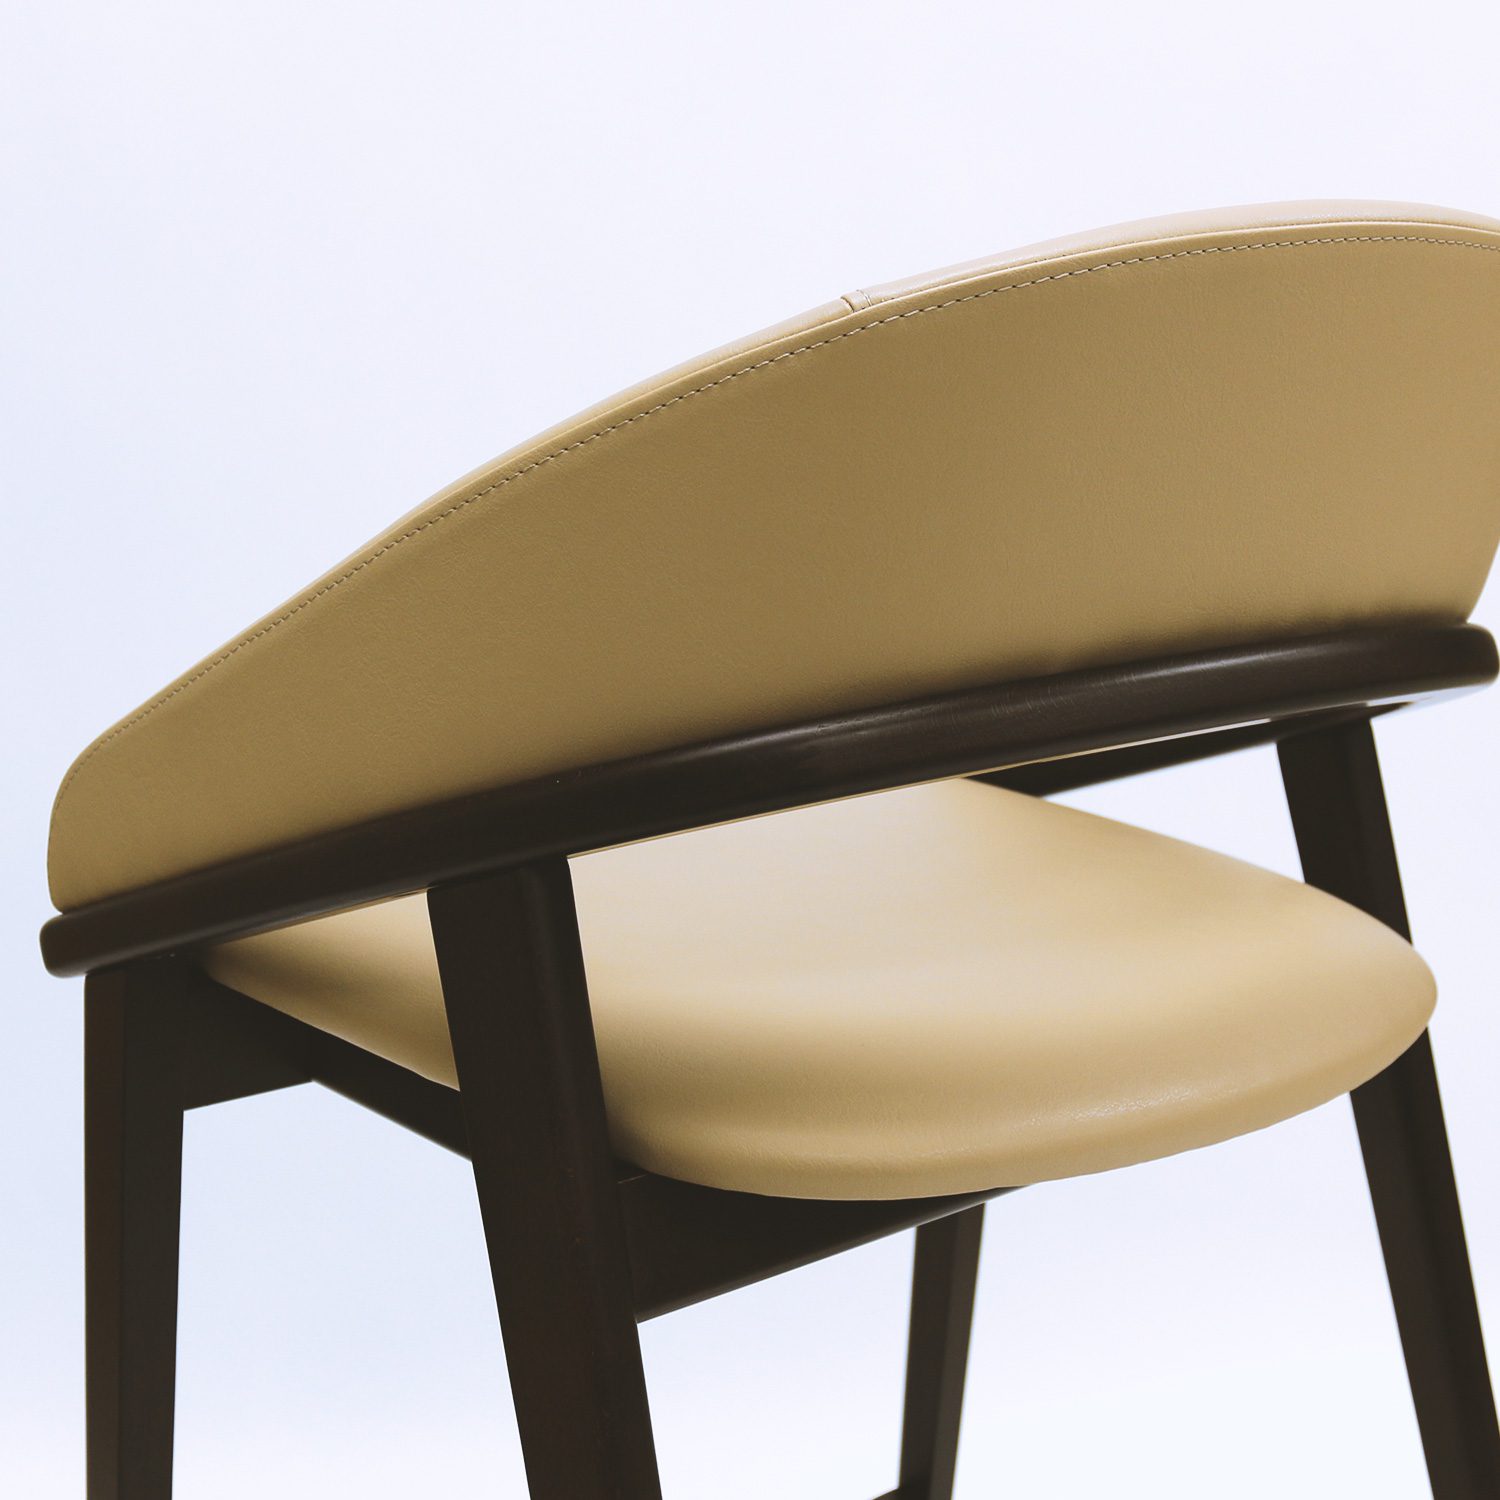
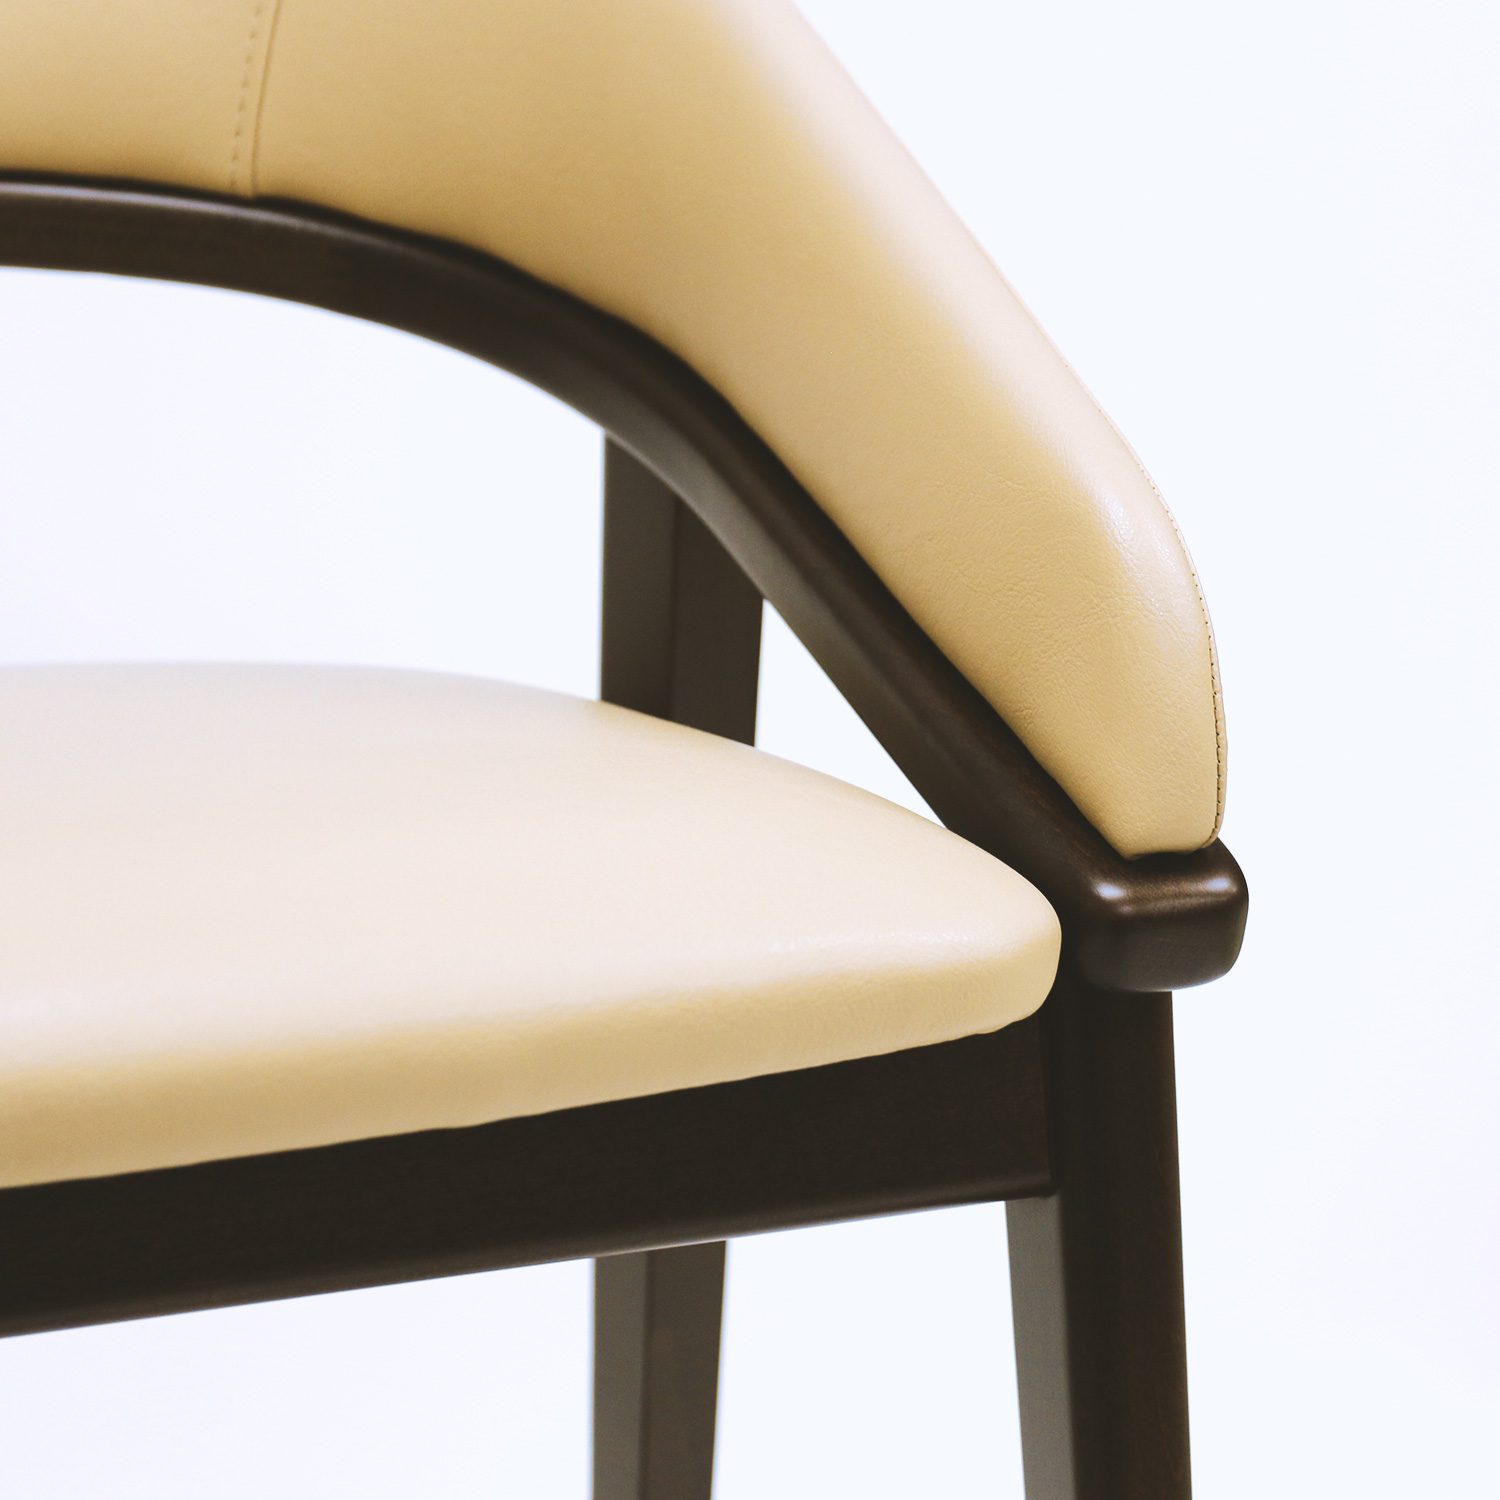
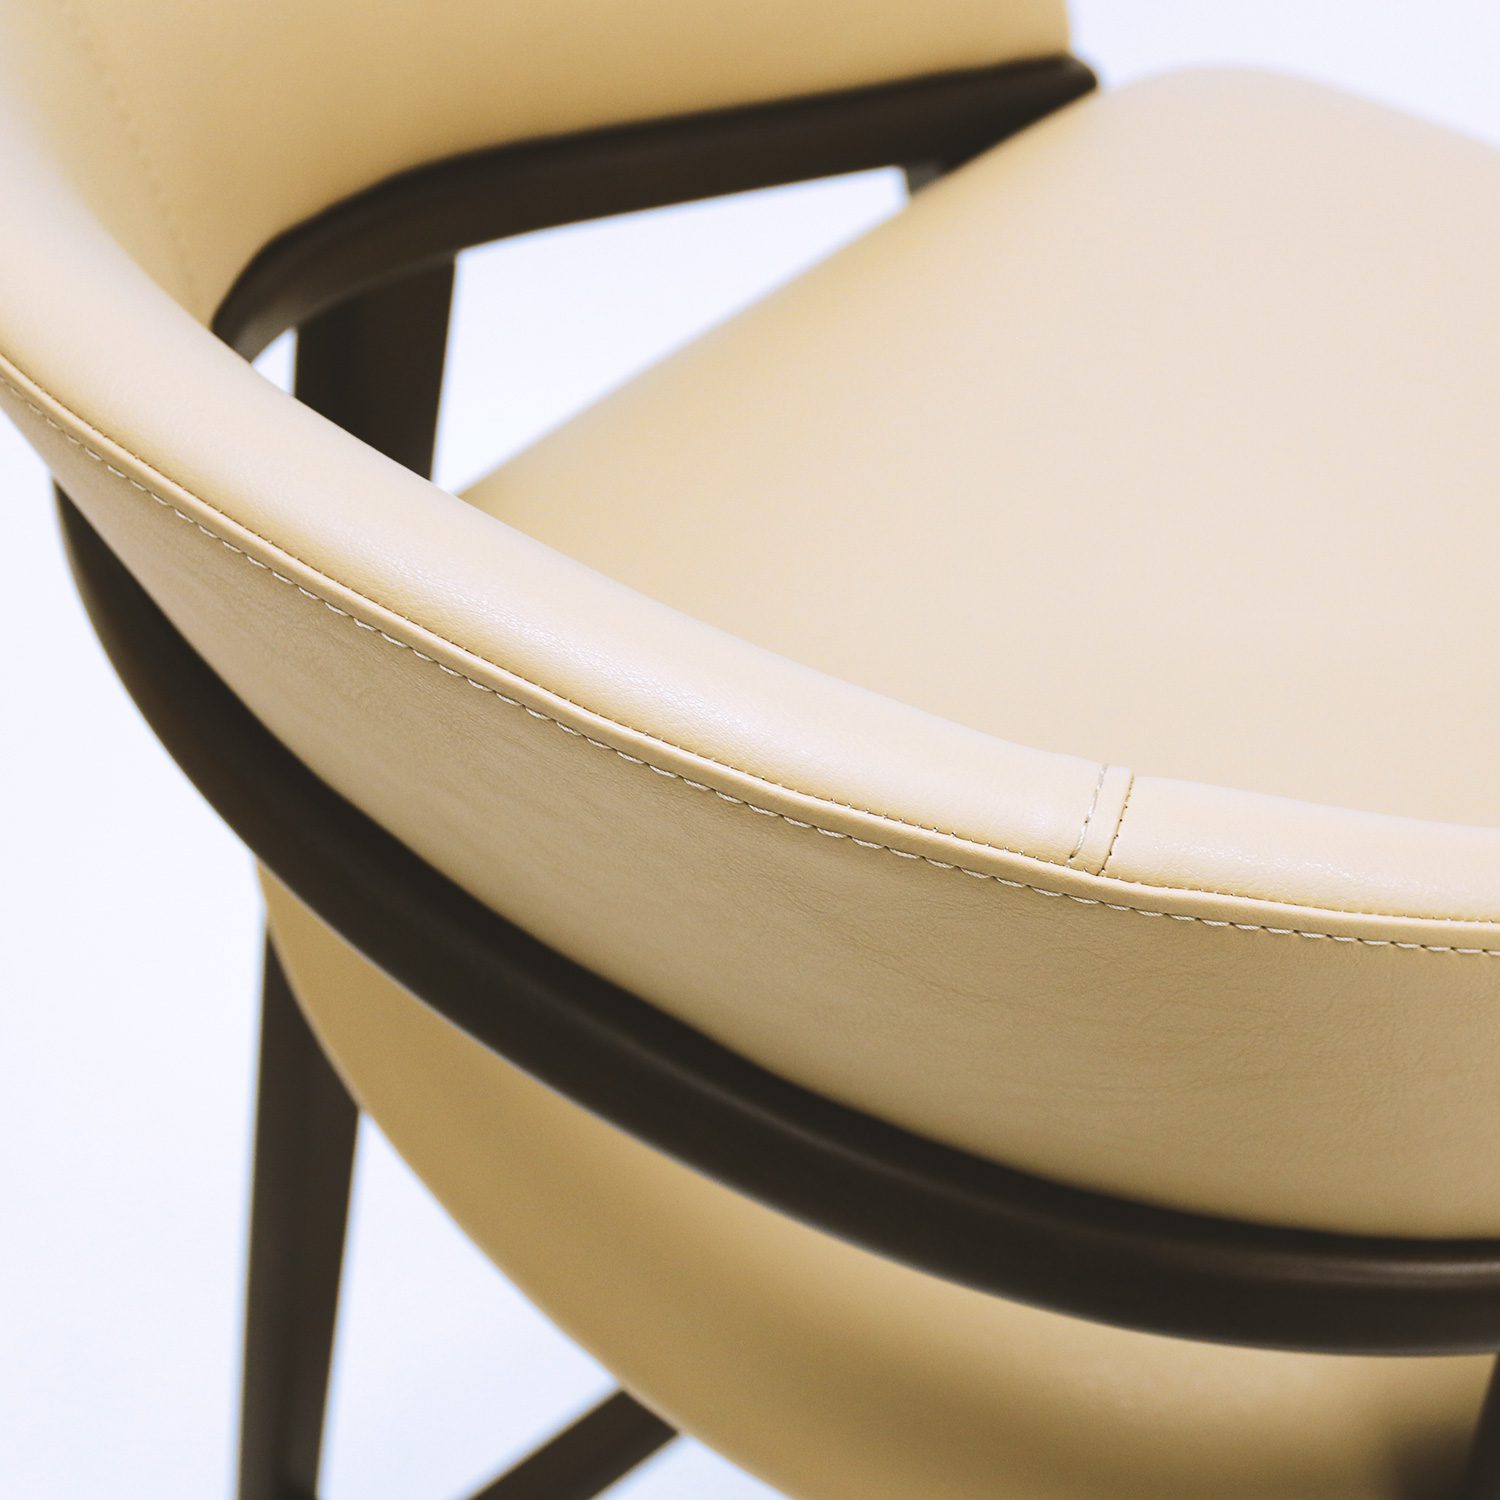
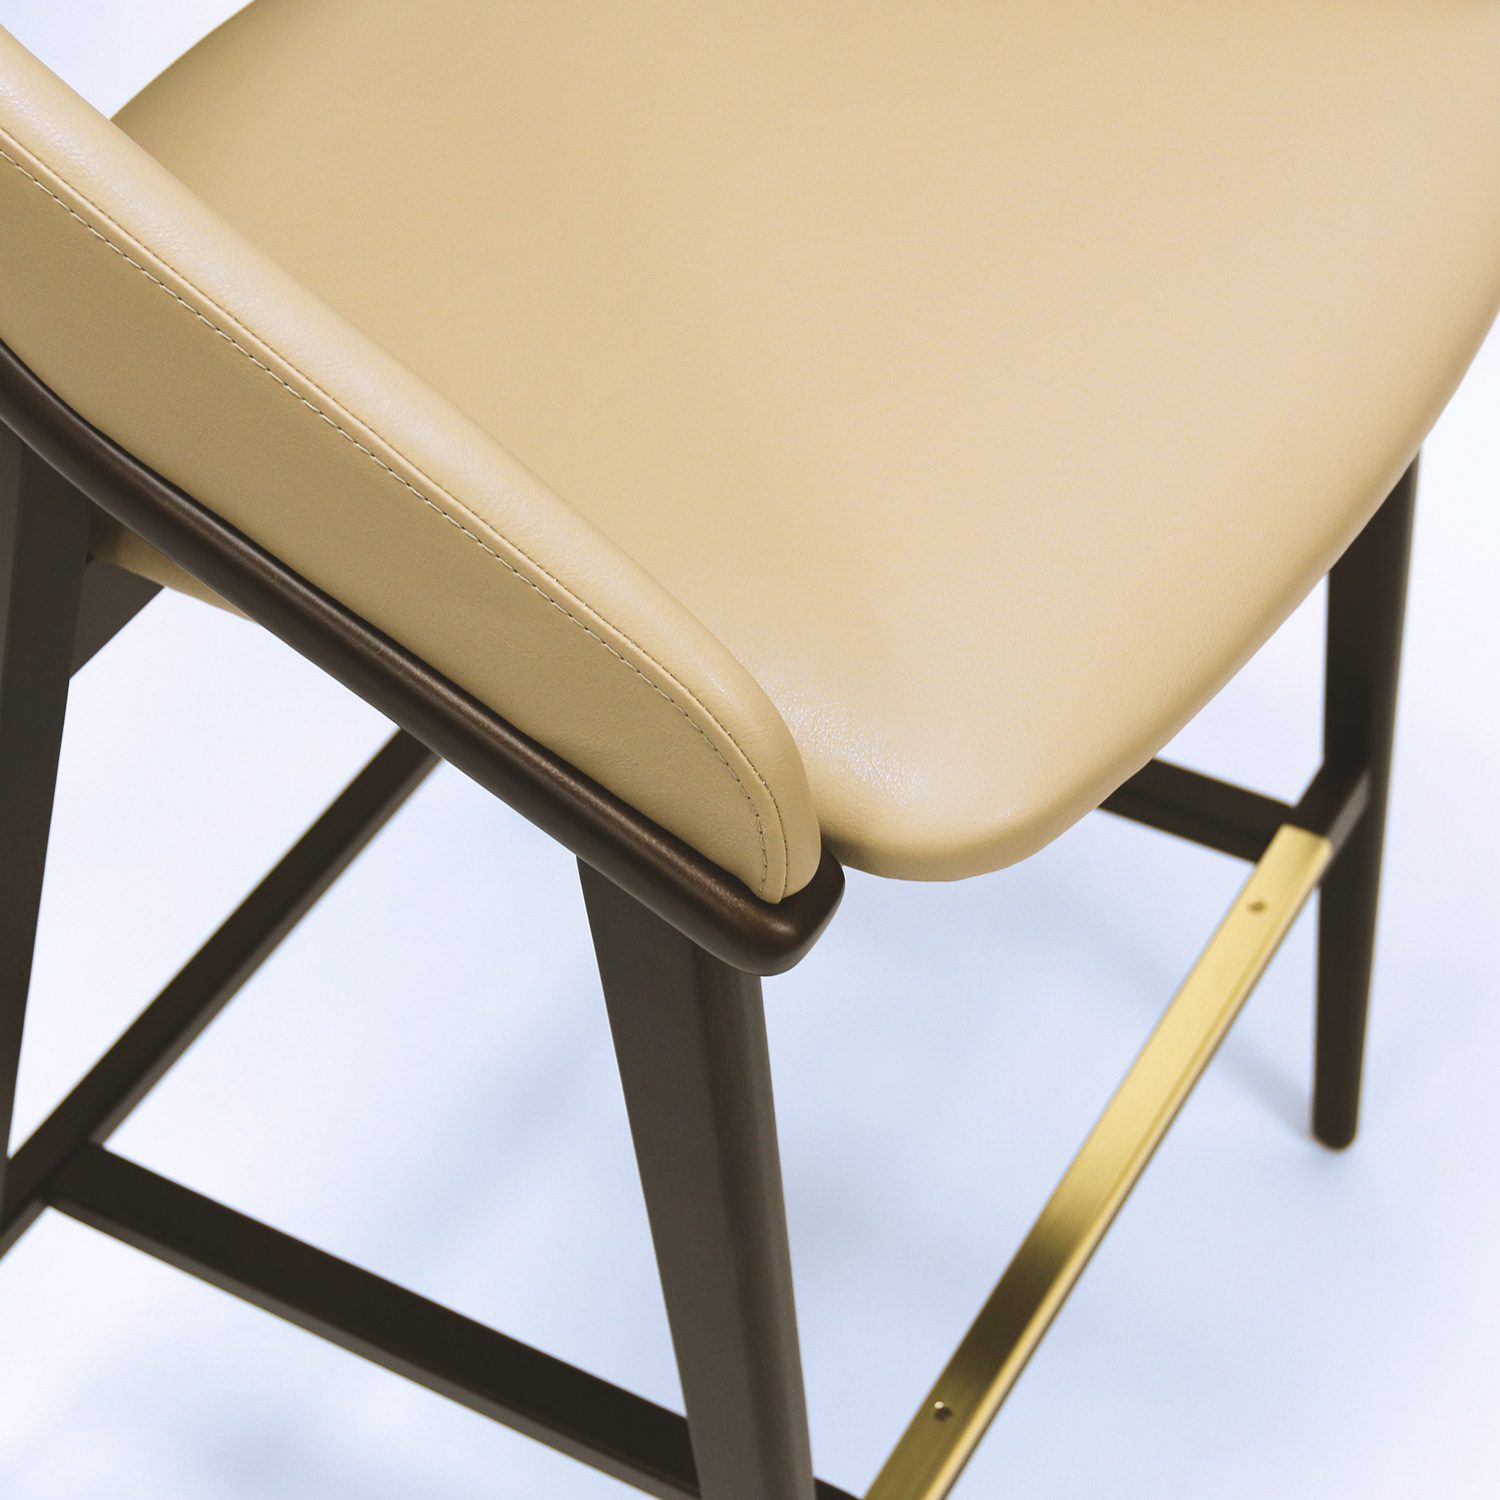
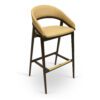
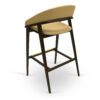
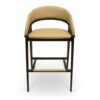
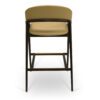
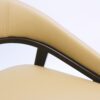
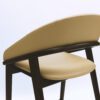
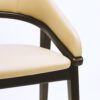
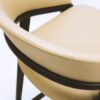
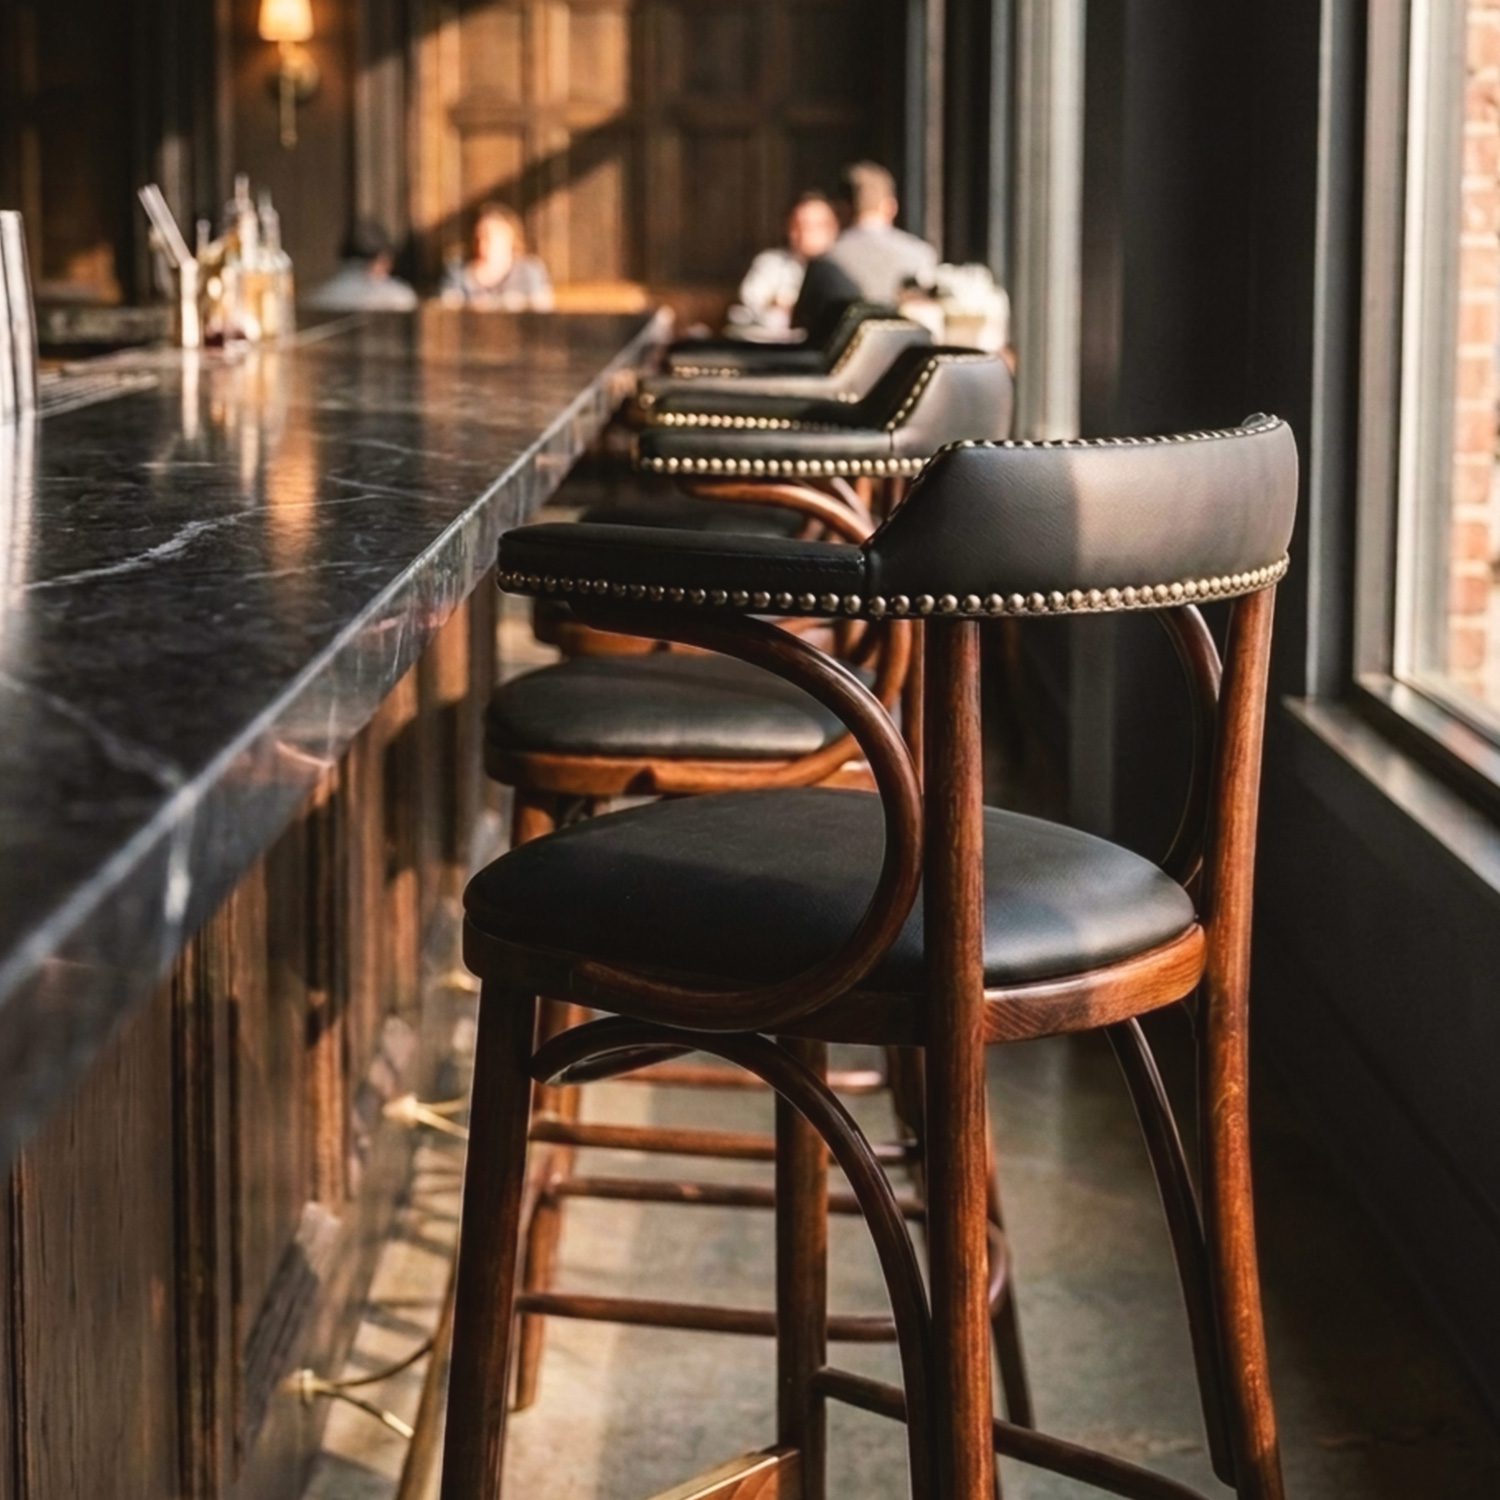
Chloe Barstool
Depth : 21.75"
Width : 22.5"
Height : 40.25"
Seat Height : 30.5"
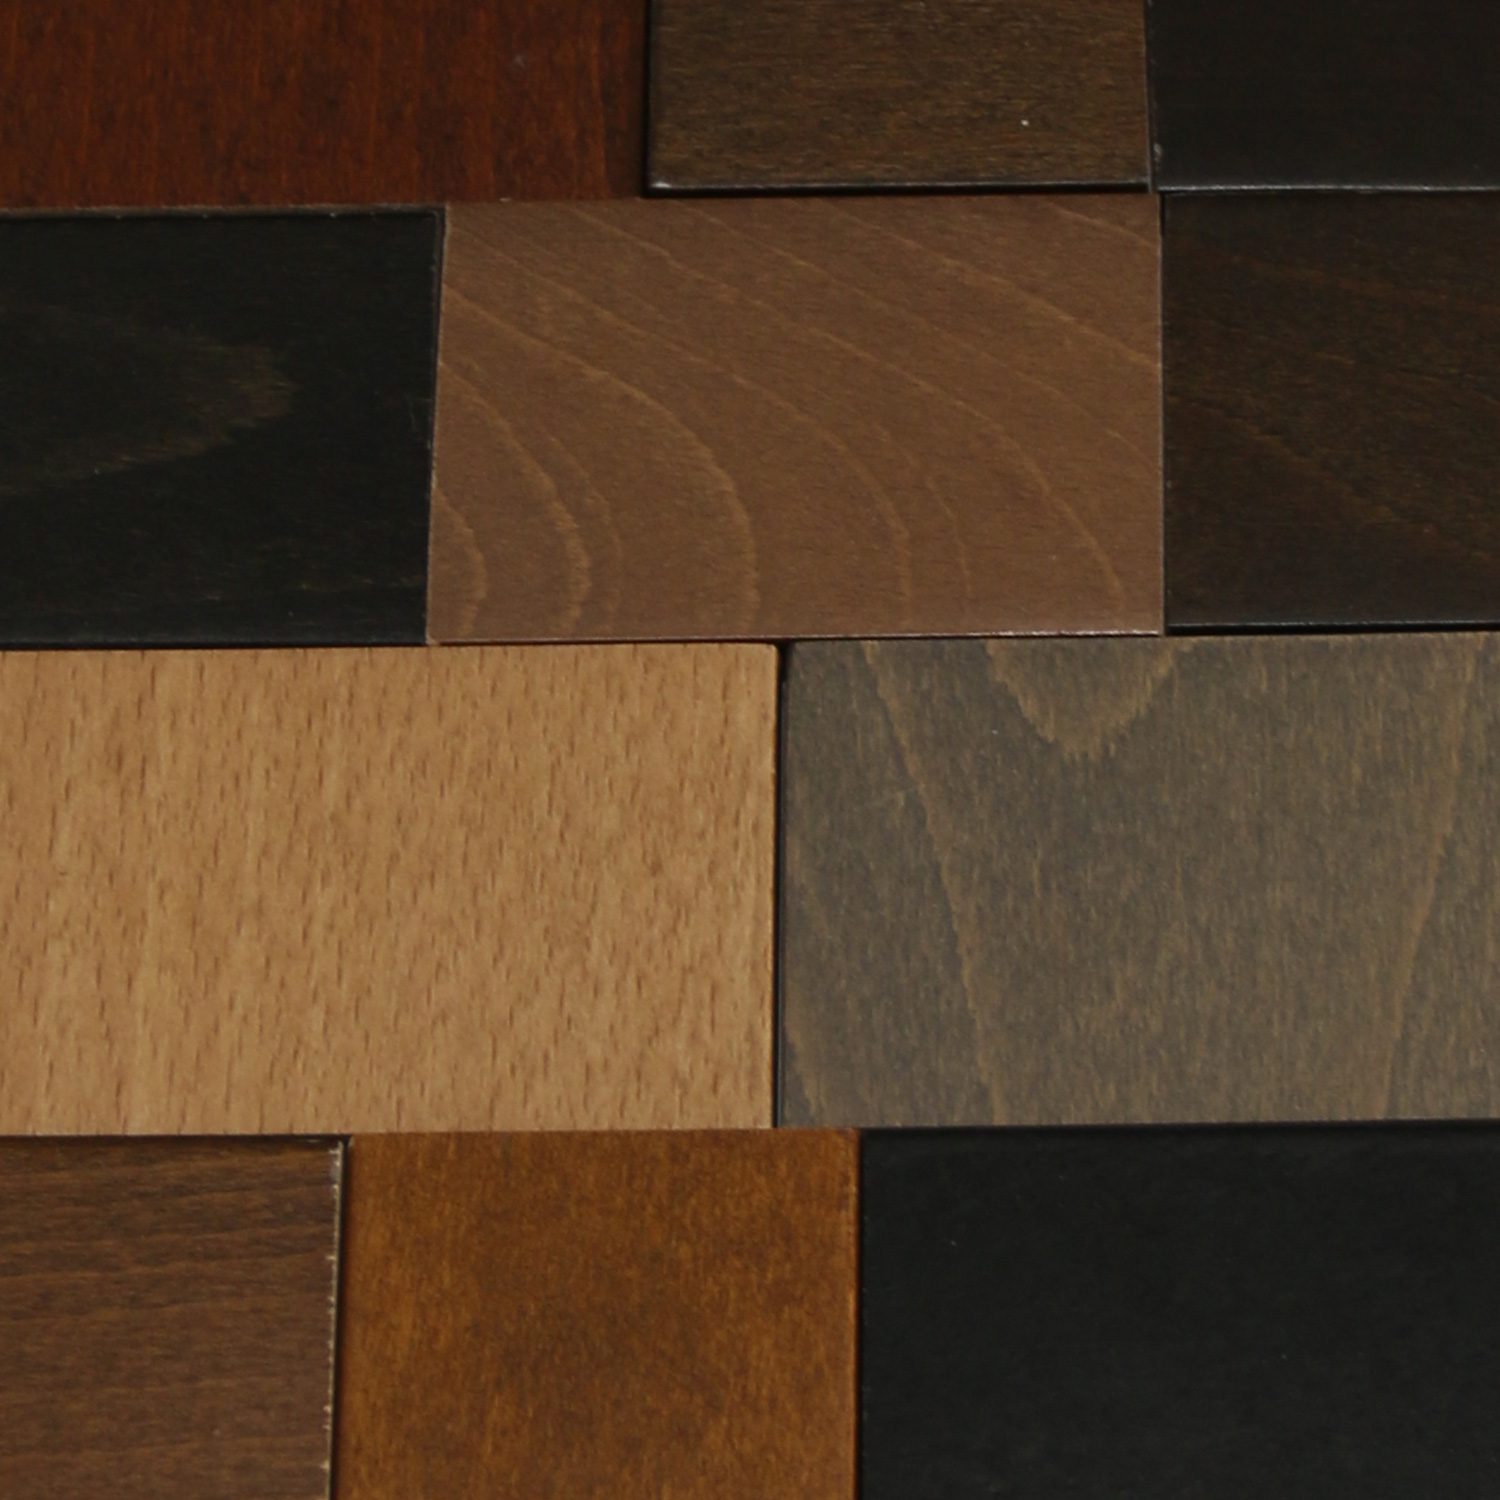
- Manufactured with European beechwood
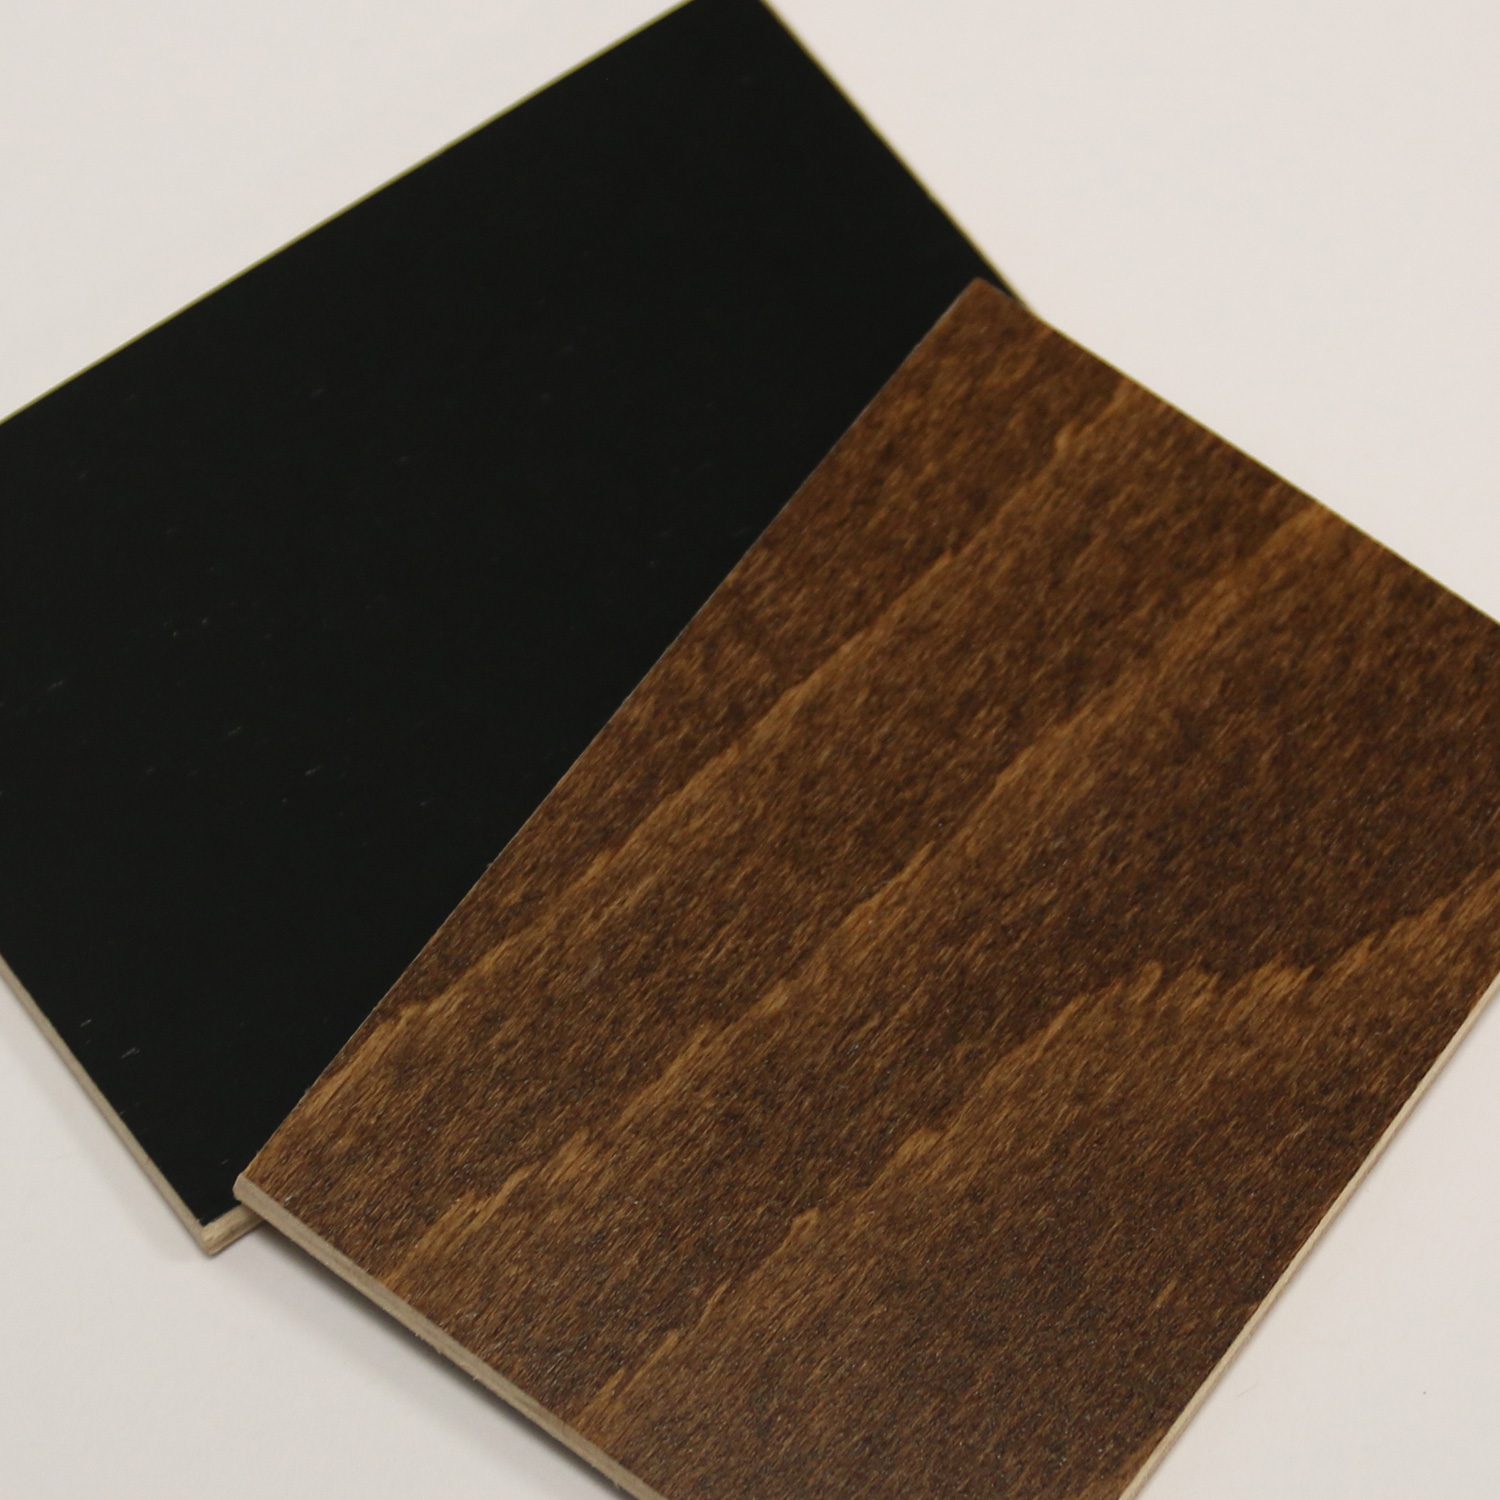
- Available in custom lacquer finish to match UV colors
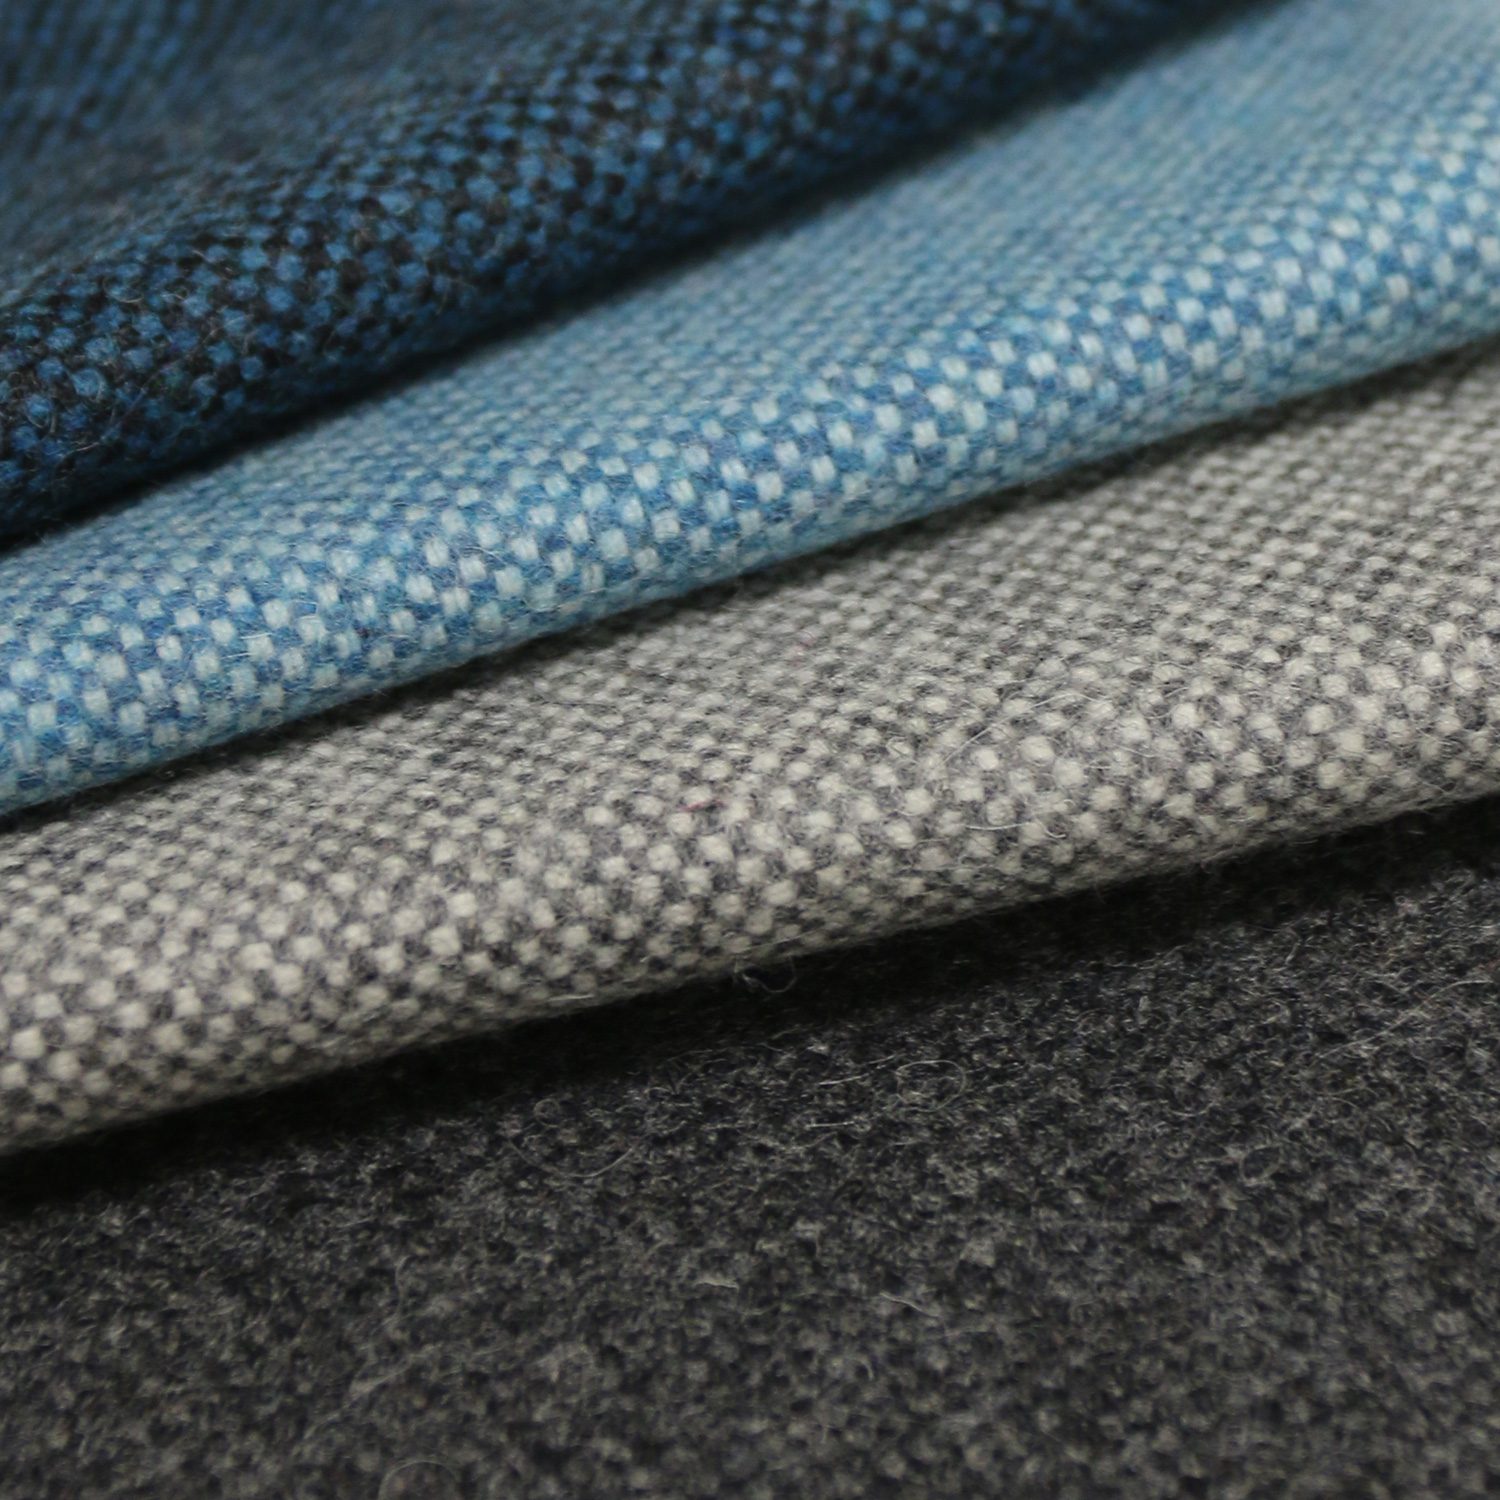
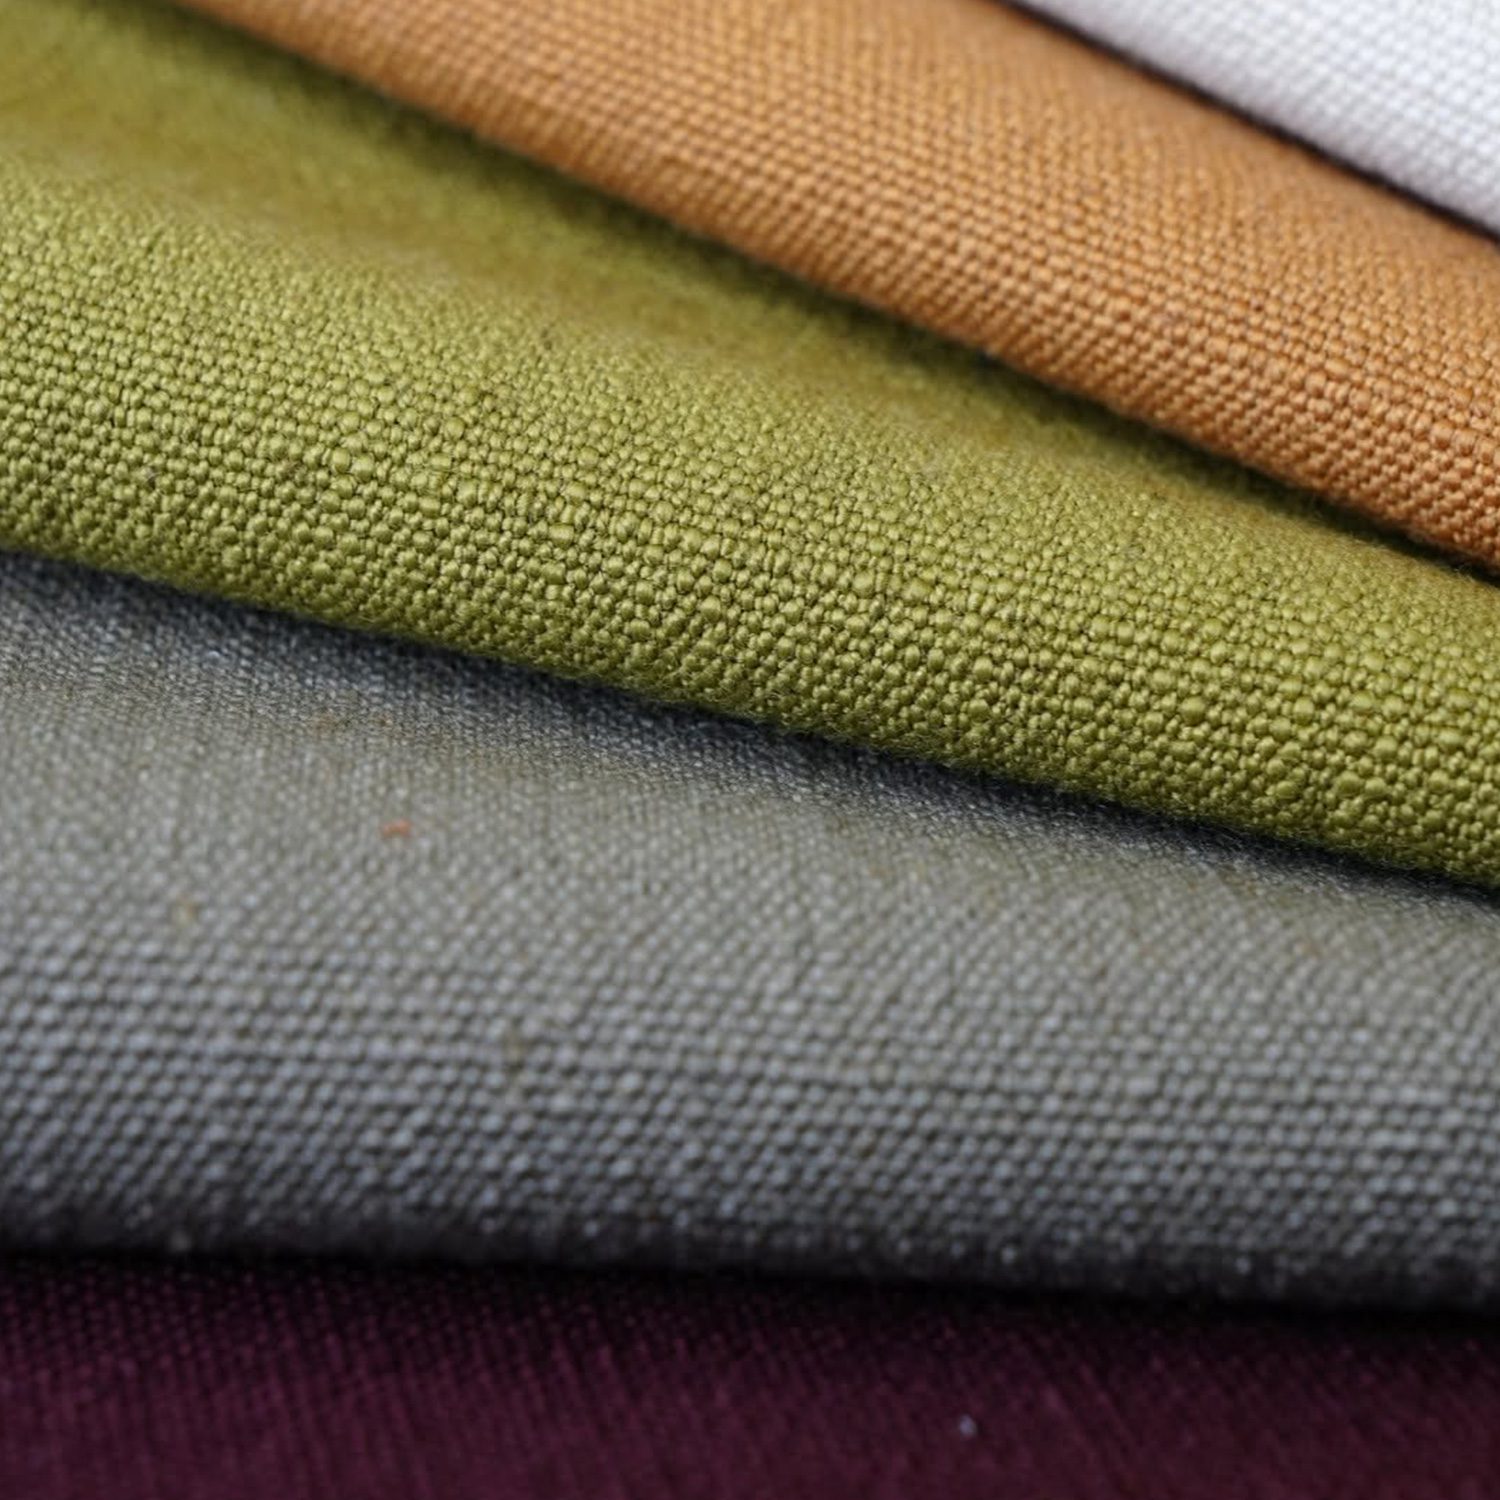
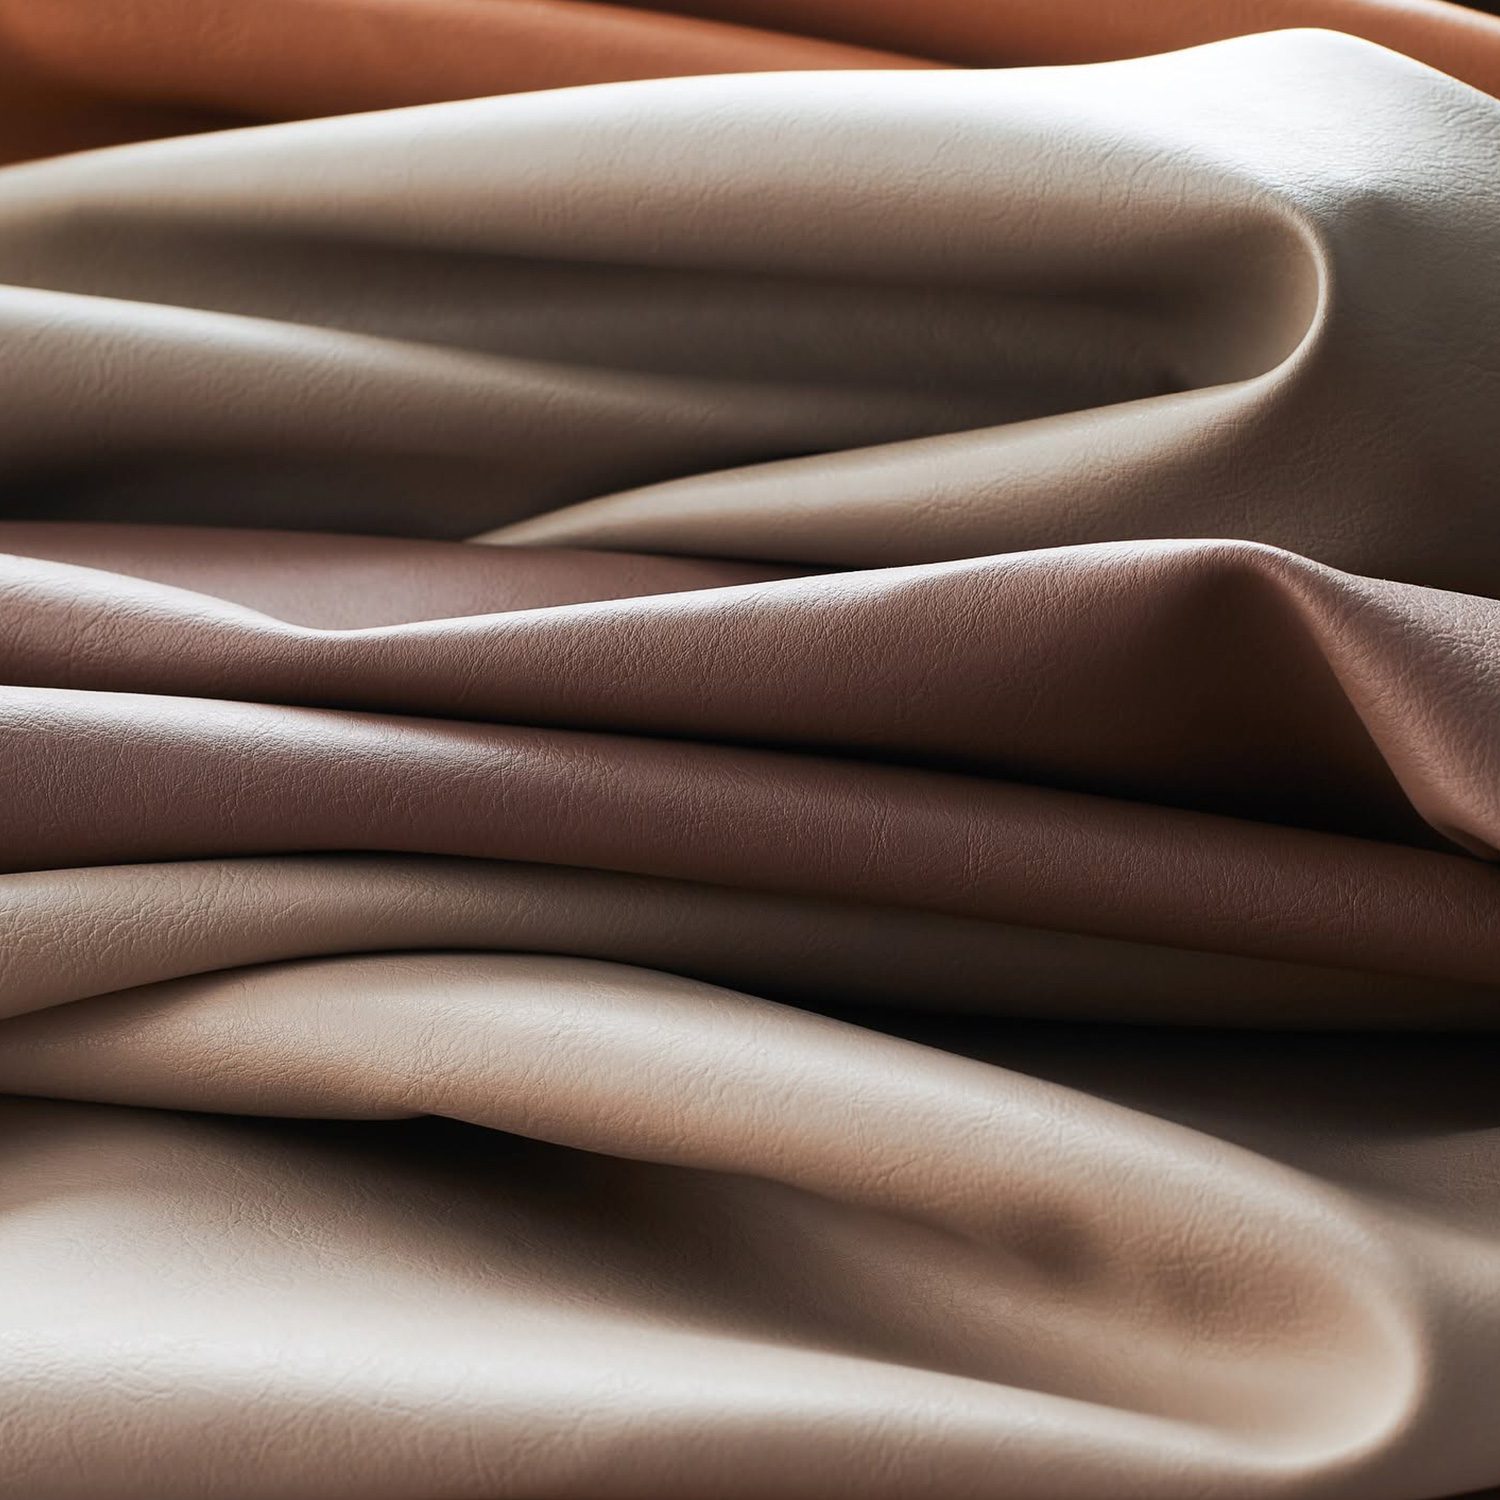
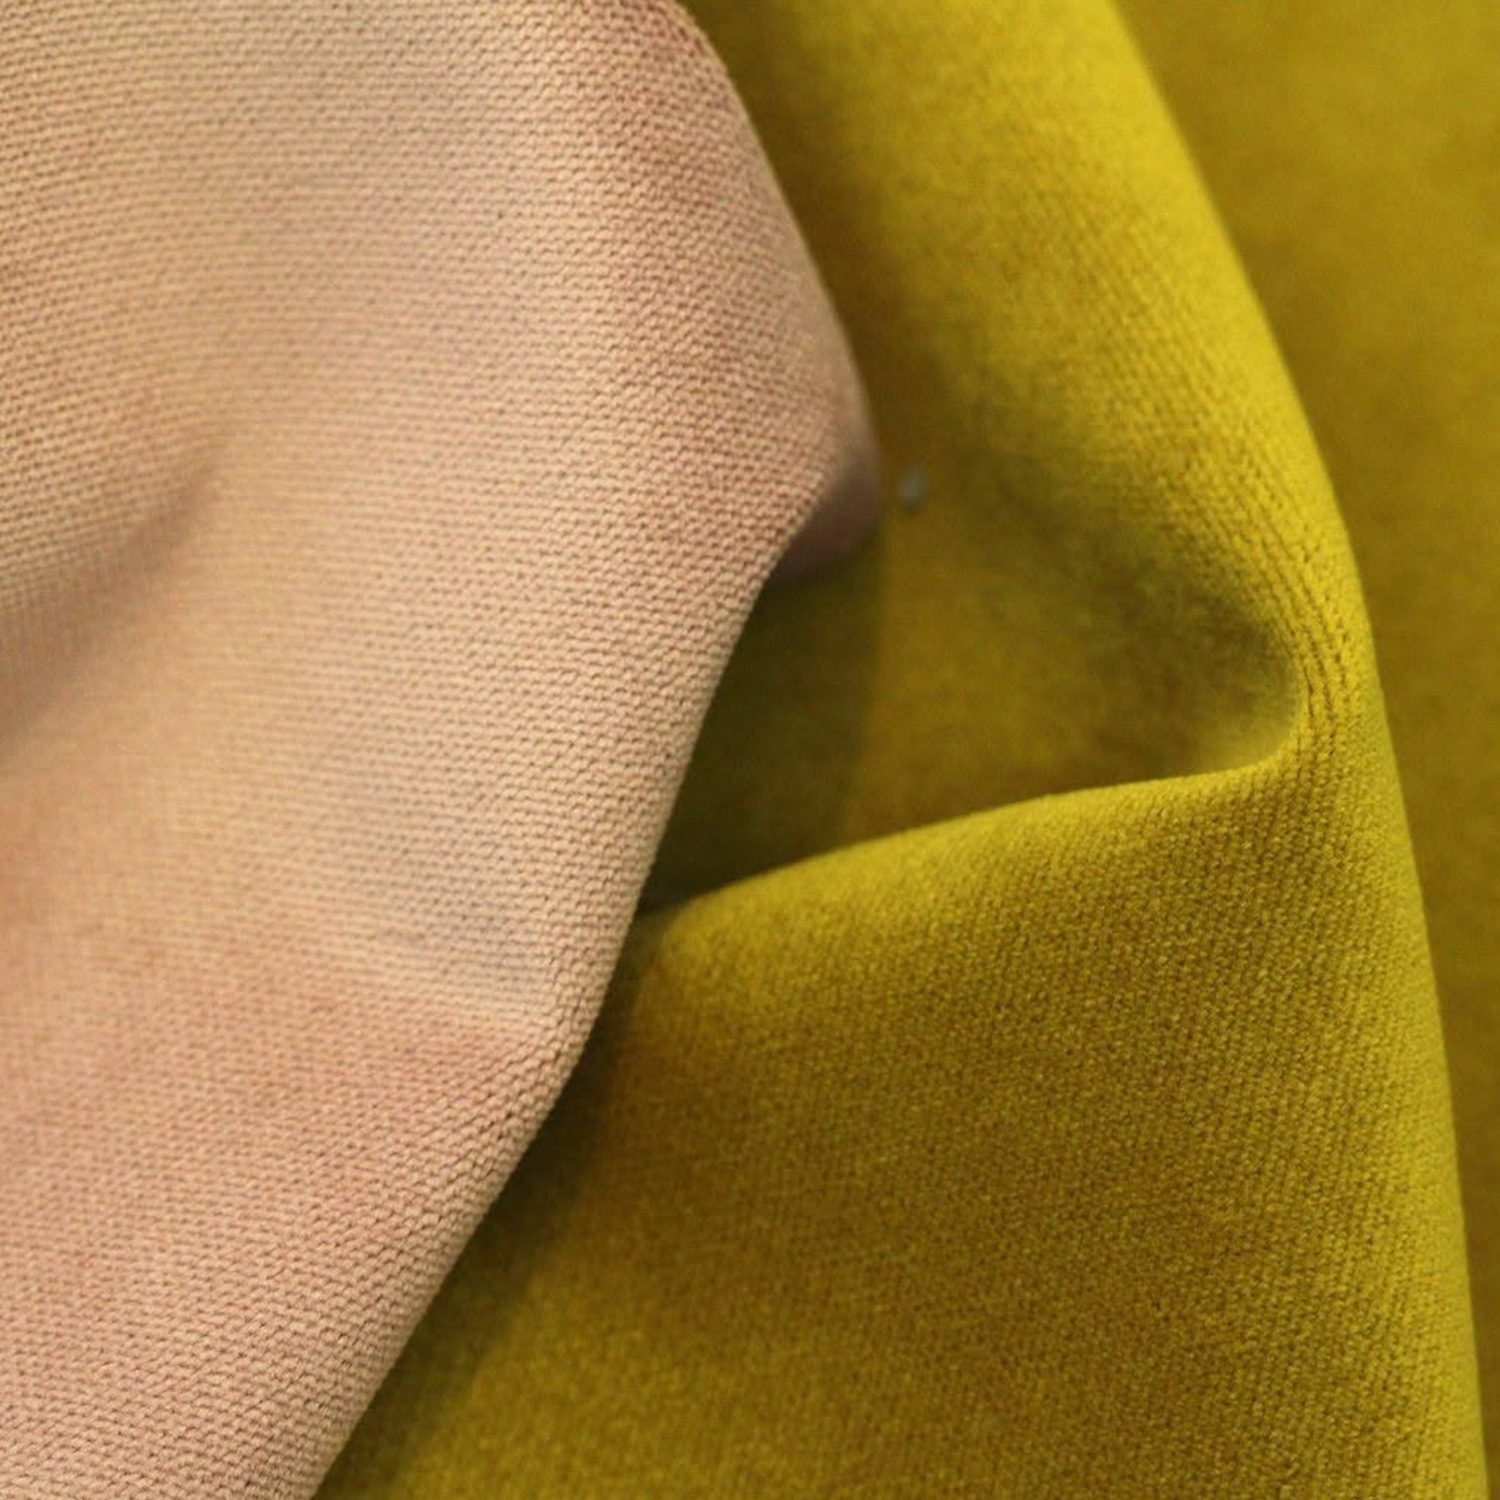
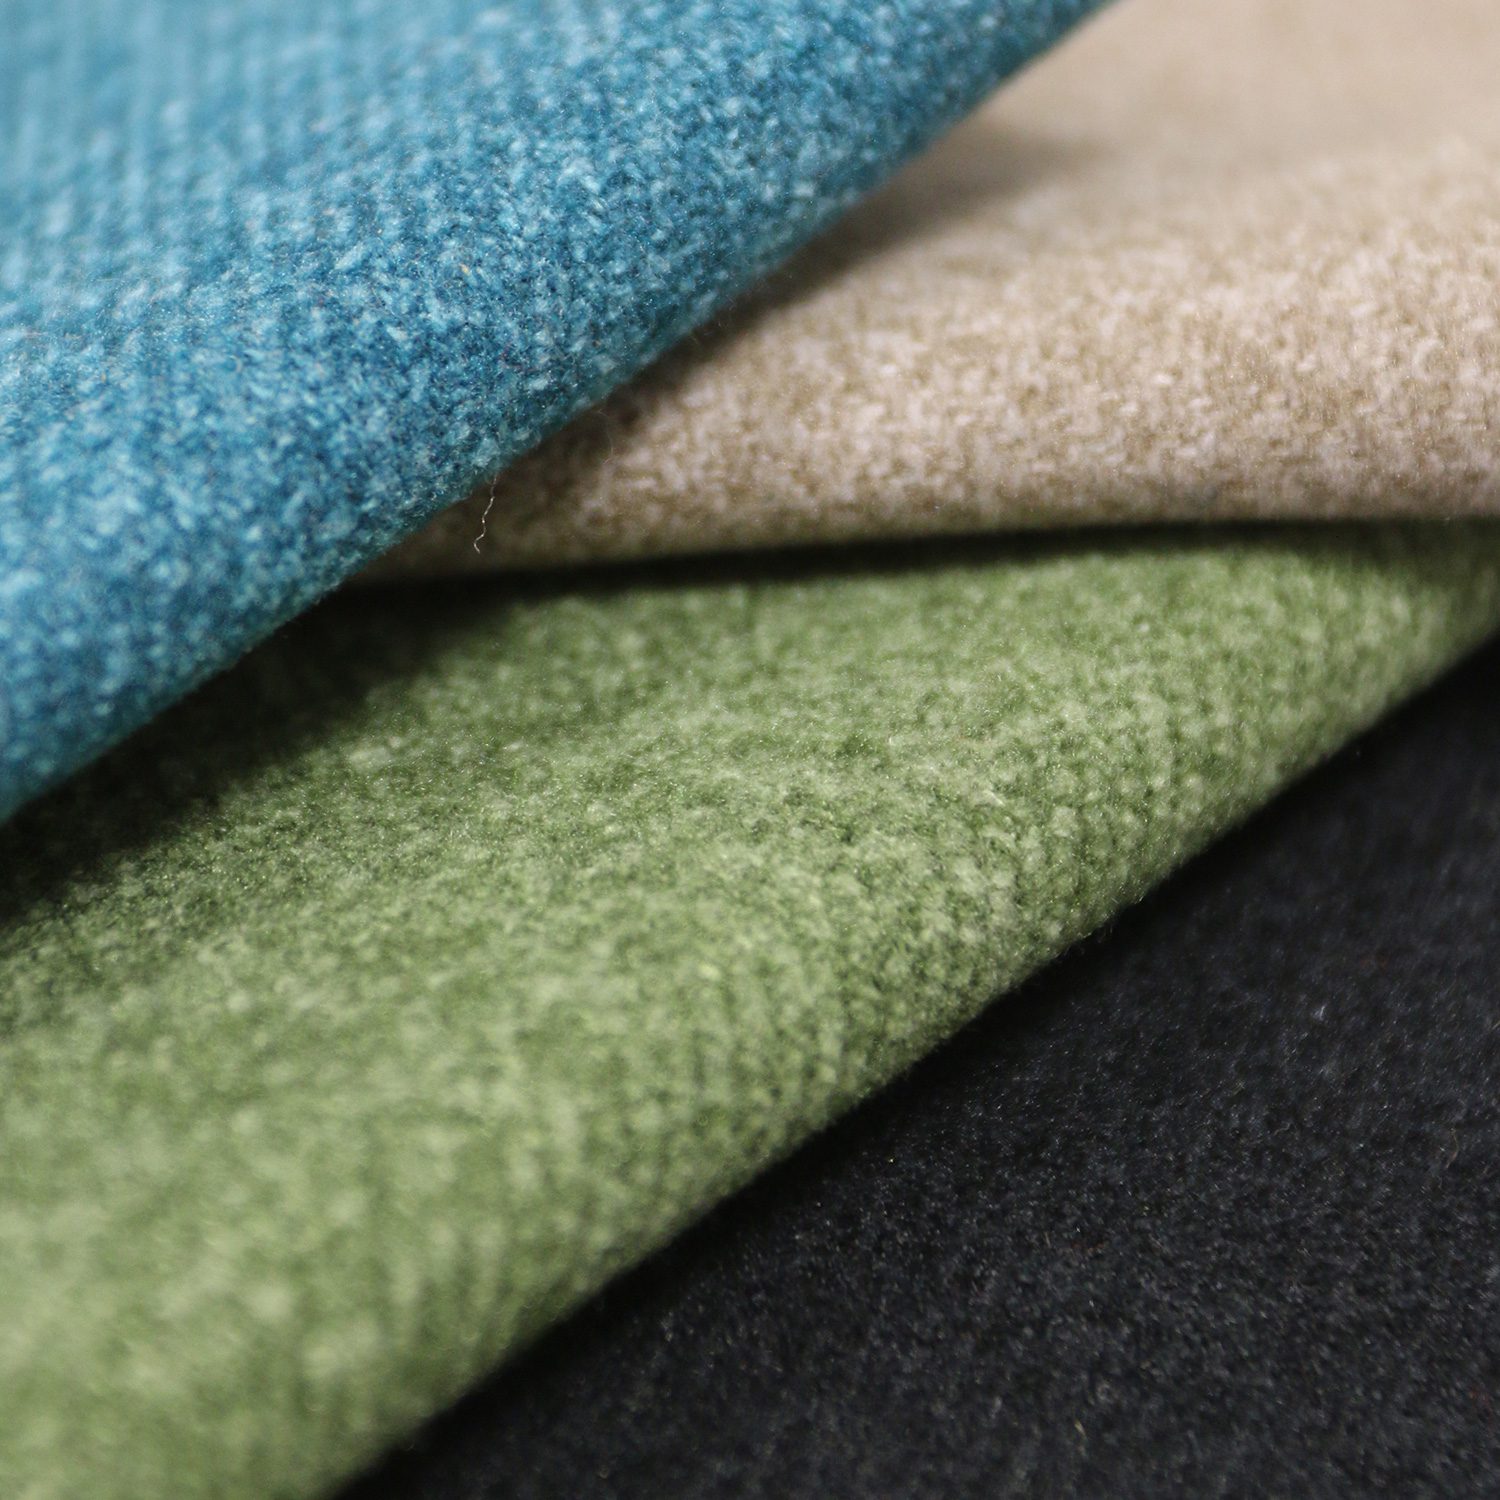
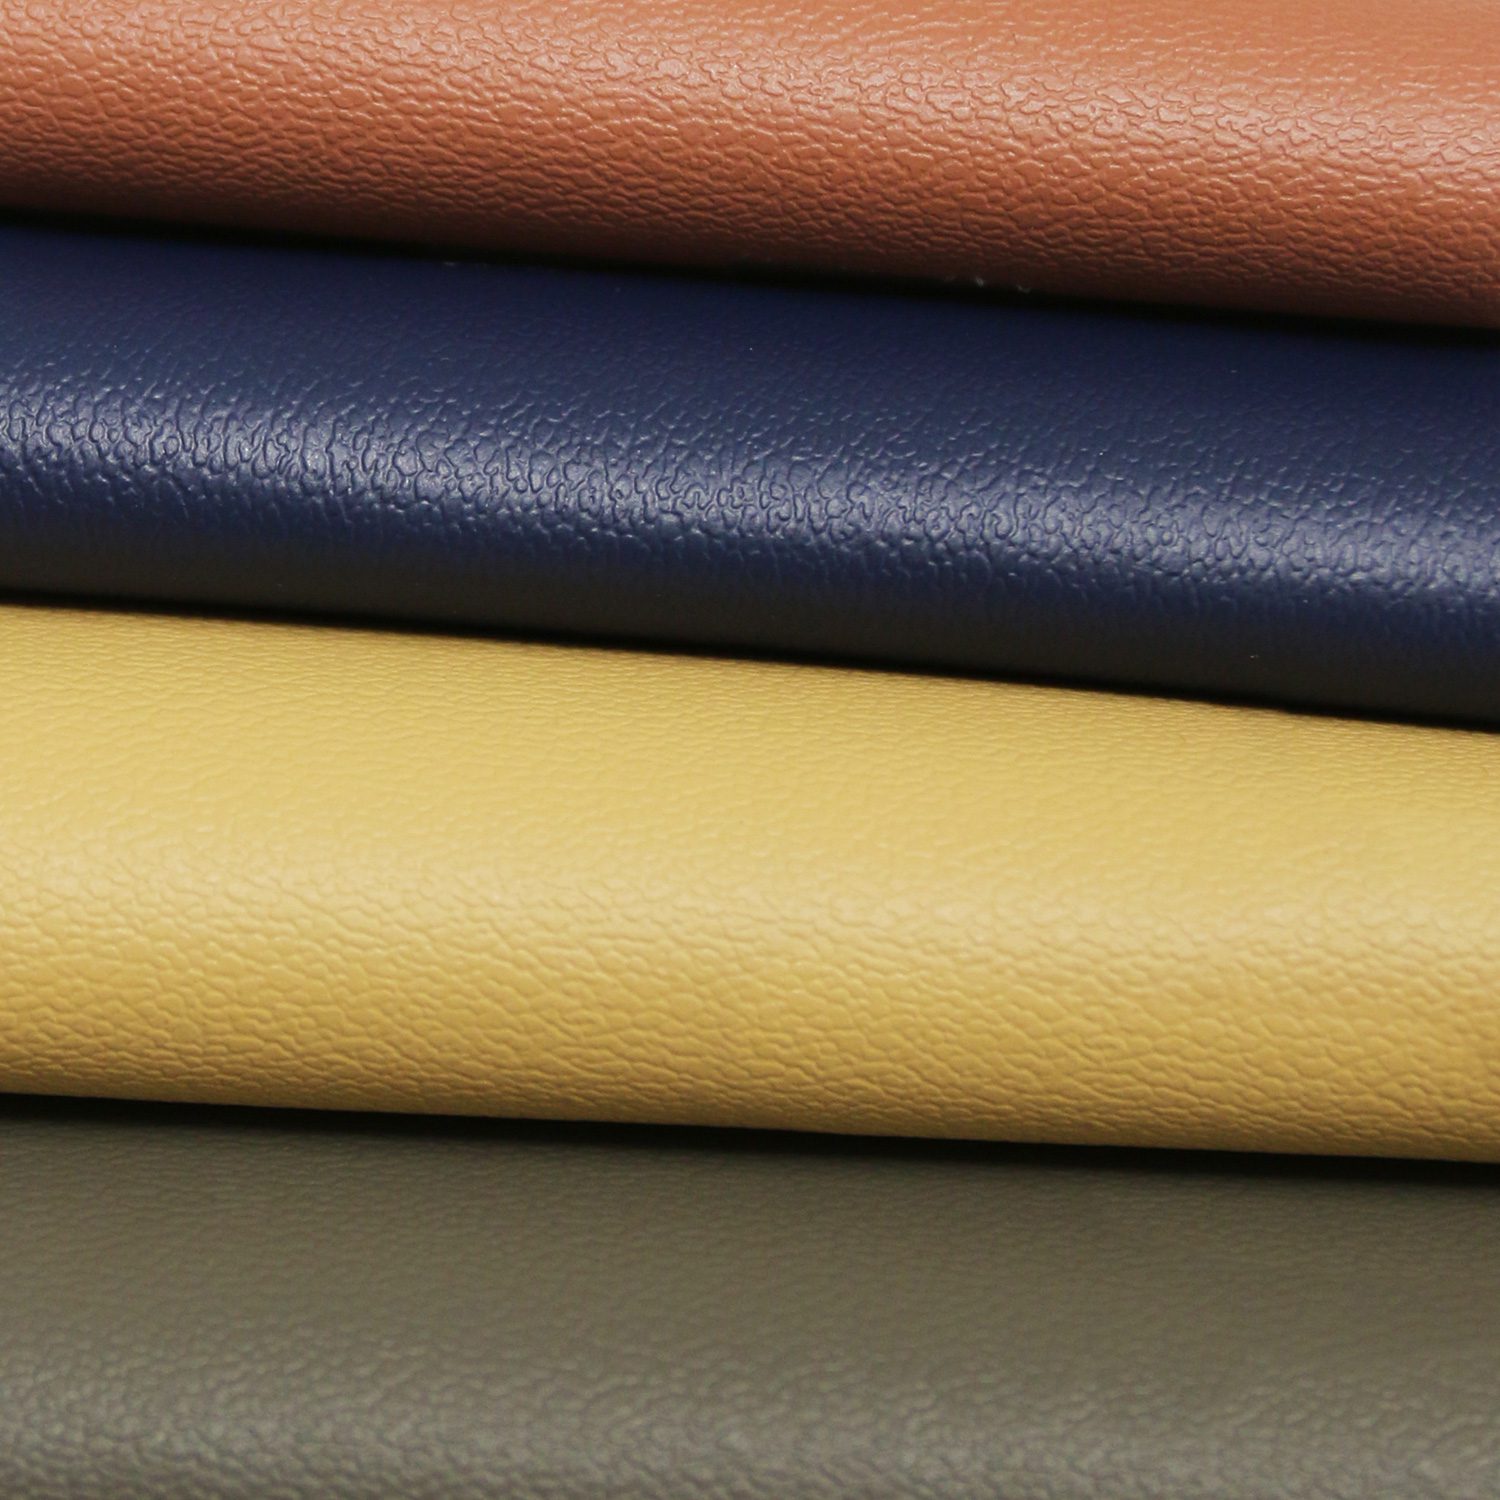
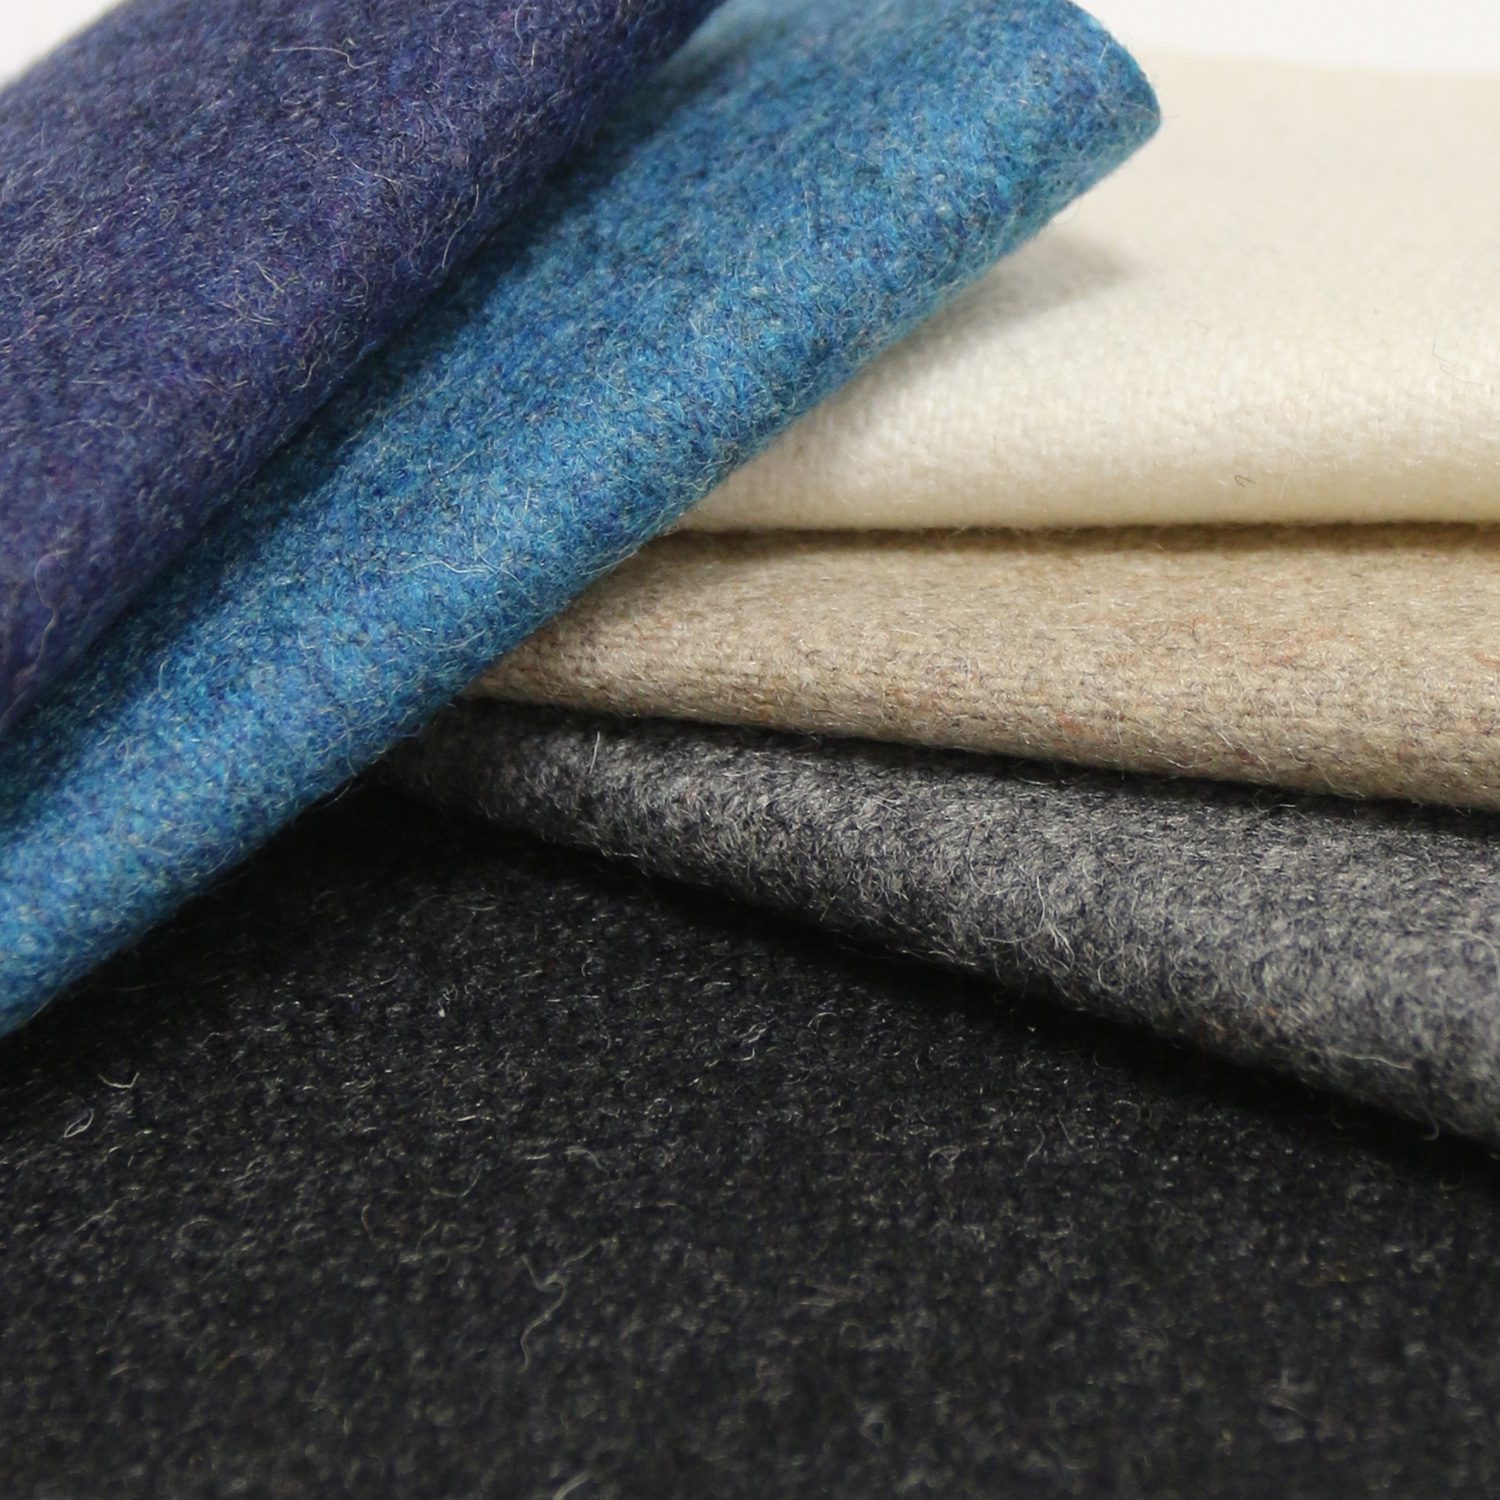
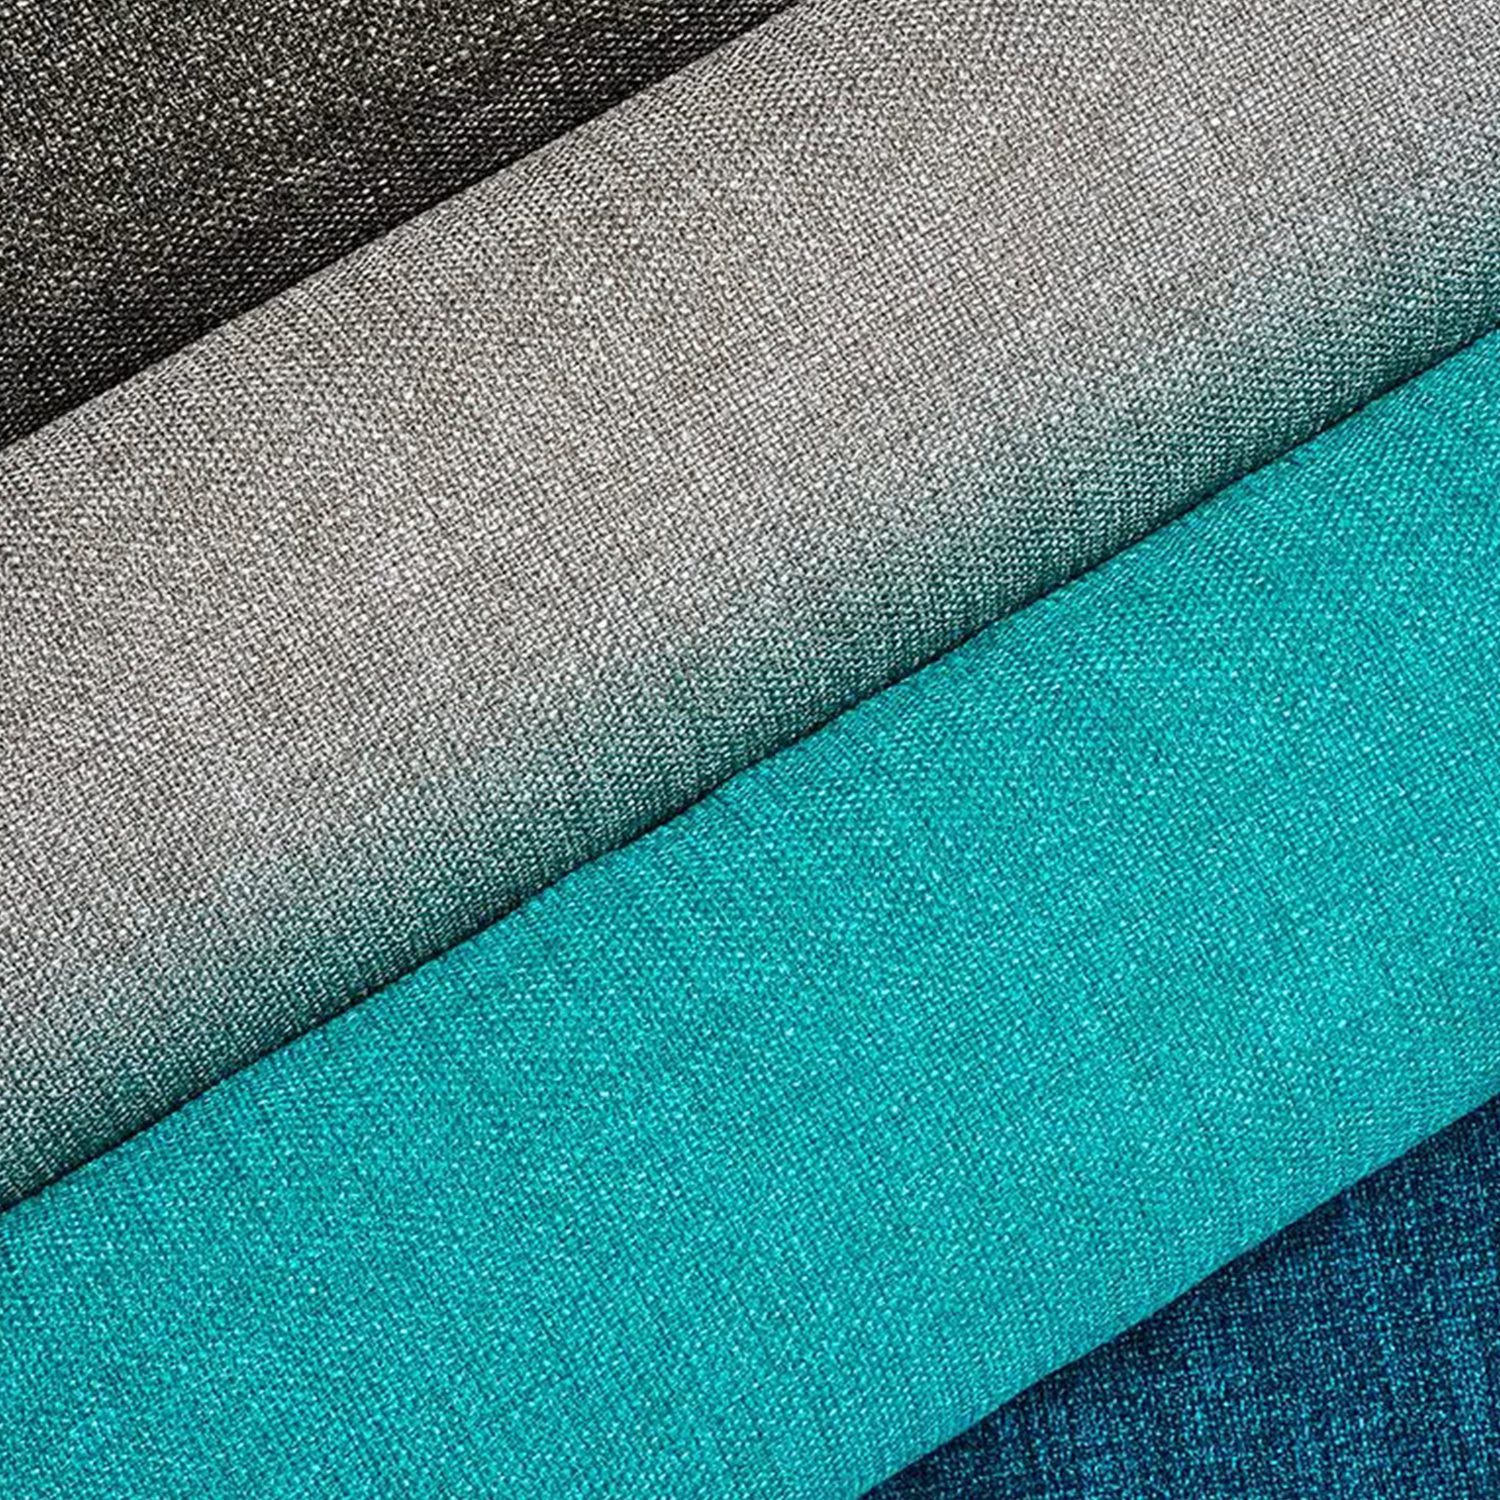
- Available in Panaz Aston, Panaz Highland or Panaz Noble fabric collections or COM only
- This item is part of the Vida collection and carries a five (5) year structural warranty
Why Mobile Gaming Security Is Evolving Fast, According to Casizoids
Mobile gaming has grown into one of the most active digital ecosystems on the planet, with over 3.2 billion mobile gamers recorded globally by 2023 and annual revenues surpassing $90 billion. That scale brings with it an equally significant security challenge. Unlike desktop or console gaming, mobile platforms introduce unique vulnerabilities — from insecure app stores and device fragmentation to unsecured Wi-Fi connections and poorly implemented in-app payment systems. Security in this space is not standing still, and analysts and platform observers including Casizoids have been tracking a measurable acceleration in how the industry is responding to these threats.
The Threat Landscape Has Shifted Dramatically Since 2020
Between 2020 and 2024, mobile gaming became a primary target for cybercriminals in ways that were not fully anticipated even five years ago. The explosion of free-to-play titles with real-money microtransactions created a financial attack surface that rivals traditional e-commerce. Credential stuffing attacks — where stolen username and password combinations from unrelated data breaches are tested against gaming accounts — increased by an estimated 85% across mobile platforms between 2021 and 2023, according to data from Akamai’s State of the Internet reports.
Beyond account takeovers, mobile games have become vectors for malware distribution. Fake APK files mimicking popular titles have been documented delivering banking trojans, spyware, and adware to millions of devices. In 2022, ESET researchers identified over 35 fake gaming apps on third-party Android stores that contained the Joker malware family, capable of silently subscribing users to premium SMS services. Google Play Protect and Apple’s App Review process have improved, but neither is impenetrable. The challenge is compounded by the fact that mobile operating systems update inconsistently across the global device ecosystem — as of 2023, a significant portion of Android devices in use were still running versions two or more major releases behind the current build.
Regulatory pressure has also shifted the conversation. The European Union’s General Data Protection Regulation (GDPR), enforced since May 2018, imposed strict requirements on how user data is collected and stored — requirements that many mobile game developers initially underestimated. The UK’s Age Appropriate Design Code, which came into force in September 2021, added further obligations specifically targeting younger players. These regulations forced studios to rethink their data architecture from the ground up, which in turn created pressure to improve overall security posture.
How the Industry Is Responding With Technical and Structural Changes
Game developers and platform operators have not been passive in the face of these pressures. One of the most significant structural shifts has been the adoption of multi-factor authentication (MFA) as a standard feature rather than an optional add-on. Major mobile gaming platforms began rolling out MFA broadly from 2021 onward, and by 2023 it had become a baseline expectation for any title managing a persistent player account with stored payment credentials.
At the technical level, the industry has moved toward more rigorous implementation of transport layer security (TLS 1.3), which reduces susceptibility to man-in-the-middle attacks — a particular concern on mobile networks where users frequently connect through public or shared infrastructure. Certificate pinning, which prevents a mobile app from accepting fraudulent SSL certificates even if a device’s root certificate store has been compromised, has become more common in security-conscious titles, particularly those involving real-money transactions.
Anti-cheat technology has also matured considerably. While anti-cheat systems are often discussed in the context of competitive fairness, they serve a dual security function — detecting and blocking unauthorized code injection, which is also a technique used to extract payment credentials or manipulate game economies for financial gain. Kernel-level anti-cheat solutions, already established on PC, are beginning to find mobile equivalents, though the implementation is more complex given the restricted permissions model of iOS and Android.
Observers who follow these developments closely, including those at Casizoids, note that the most meaningful progress is happening not in individual technical patches but in how studios are integrating security into the development lifecycle itself. The DevSecOps model — where security testing is embedded at every stage of software development rather than applied as a final check — has moved from enterprise software into mobile game development, particularly among studios with international player bases subject to multiple regulatory frameworks. Those interested in how these patterns are being tracked across different gaming categories can read more at Casizoids, where ongoing analysis covers security trends across mobile and digital gaming environments.
The Role of Platform Gatekeepers and Third-Party Ecosystems
Apple and Google occupy a unique position in mobile gaming security because they control the primary distribution channels and, by extension, the baseline security standards that all developers must meet. Both companies have tightened their requirements over the past several years. Apple’s App Store Review Guidelines were updated in 2022 to impose stricter requirements on apps handling financial transactions, and Google Play introduced the Data Safety section in 2022, requiring developers to publicly disclose what user data their apps collect, share, and how it is protected.
However, the real complexity lies outside these walled gardens. Android’s open architecture allows sideloading — the installation of apps from sources other than the official Play Store — and this remains a persistent security gap. In regions where Google Play is less accessible or where regional app stores dominate, such as parts of Southeast Asia, South Asia, and China, users are exposed to a fragmented security environment where vetting standards vary significantly. This is not a theoretical problem: Kaspersky’s research teams have documented multiple campaigns specifically targeting users of regional Android app markets with gaming-themed malware.
The third-party SDK (software development kit) ecosystem presents a related challenge. Mobile games routinely integrate dozens of third-party SDKs for analytics, advertising, social login, and payment processing. Each SDK represents a potential attack surface. A vulnerability or malicious update in a widely used advertising SDK can affect thousands of games and millions of users simultaneously. The 2020 SourMint incident, in which a popular mobile SDK from Mintegral was found to engage in potentially fraudulent and privacy-violating behavior, illustrated exactly how this supply chain risk operates in practice.
Regulatory bodies are beginning to address this indirectly. The EU’s Digital Markets Act, which began applying to designated gatekeepers in March 2024, includes provisions that could affect how app store operators manage third-party integrations and security obligations. Whether these provisions will meaningfully reduce SDK-related risks remains to be seen, but the legislative direction is clear: platform accountability is expanding.
What Drives the Pace of Change — and What Still Lags Behind
The acceleration in mobile gaming security is being driven by a combination of financial incentives, regulatory enforcement, and reputational risk. When a major gaming account breach occurs, the direct costs — fraud reimbursement, legal exposure, customer support — are substantial. But the reputational damage to a studio’s player trust can be more lasting than any single financial hit. This has made security investment easier to justify internally in ways that were harder to argue before high-profile incidents became regular news.
Biometric authentication has emerged as one of the more user-friendly security advances in this space. Face ID and fingerprint authentication, now standard on most mid-to-high-end smartphones, are increasingly being used to gate in-app purchases and account changes. This reduces friction compared to traditional password-based verification while providing a meaningful security improvement — particularly for younger users who are statistically less likely to use strong, unique passwords.
Casizoids has noted that one area where progress remains uneven is in how smaller independent studios handle security. Large publishers with dedicated security teams and compliance departments have made substantial improvements. But the mobile gaming market includes tens of thousands of studios, many of them small operations with limited resources. For these developers, security is often reactive rather than proactive — addressed after an incident rather than built in from the start. Industry organizations and platform operators have begun producing more accessible security guidance specifically for smaller developers, but adoption remains inconsistent.
Artificial intelligence is beginning to play a role in both attack and defense. On the defensive side, behavioral analytics powered by machine learning are being used to detect anomalous account activity — unusual login locations, atypical purchase patterns, or rapid in-game actions that suggest automated exploitation. These systems can flag or block suspicious activity faster than any manual review process. On the offensive side, AI is enabling more sophisticated phishing campaigns and automated credential testing, which means the defensive applications need to evolve continuously to remain effective.
Mobile gaming security is evolving fast because the stakes have grown fast. The combination of real financial transactions, large and often young user bases, complex technical ecosystems, and expanding regulatory frameworks has created a pressure environment in which standing still is not a viable option. The industry has made genuine progress — in authentication standards, data handling practices, and development methodology — but the threat environment is evolving in parallel. The studios and platforms that treat security as a continuous engineering discipline rather than a compliance checkbox are the ones best positioned to protect their players as the mobile gaming landscape continues to expand.
Other Products in Series


-
FOLLOW US
-

-

-

-